Business Assessment
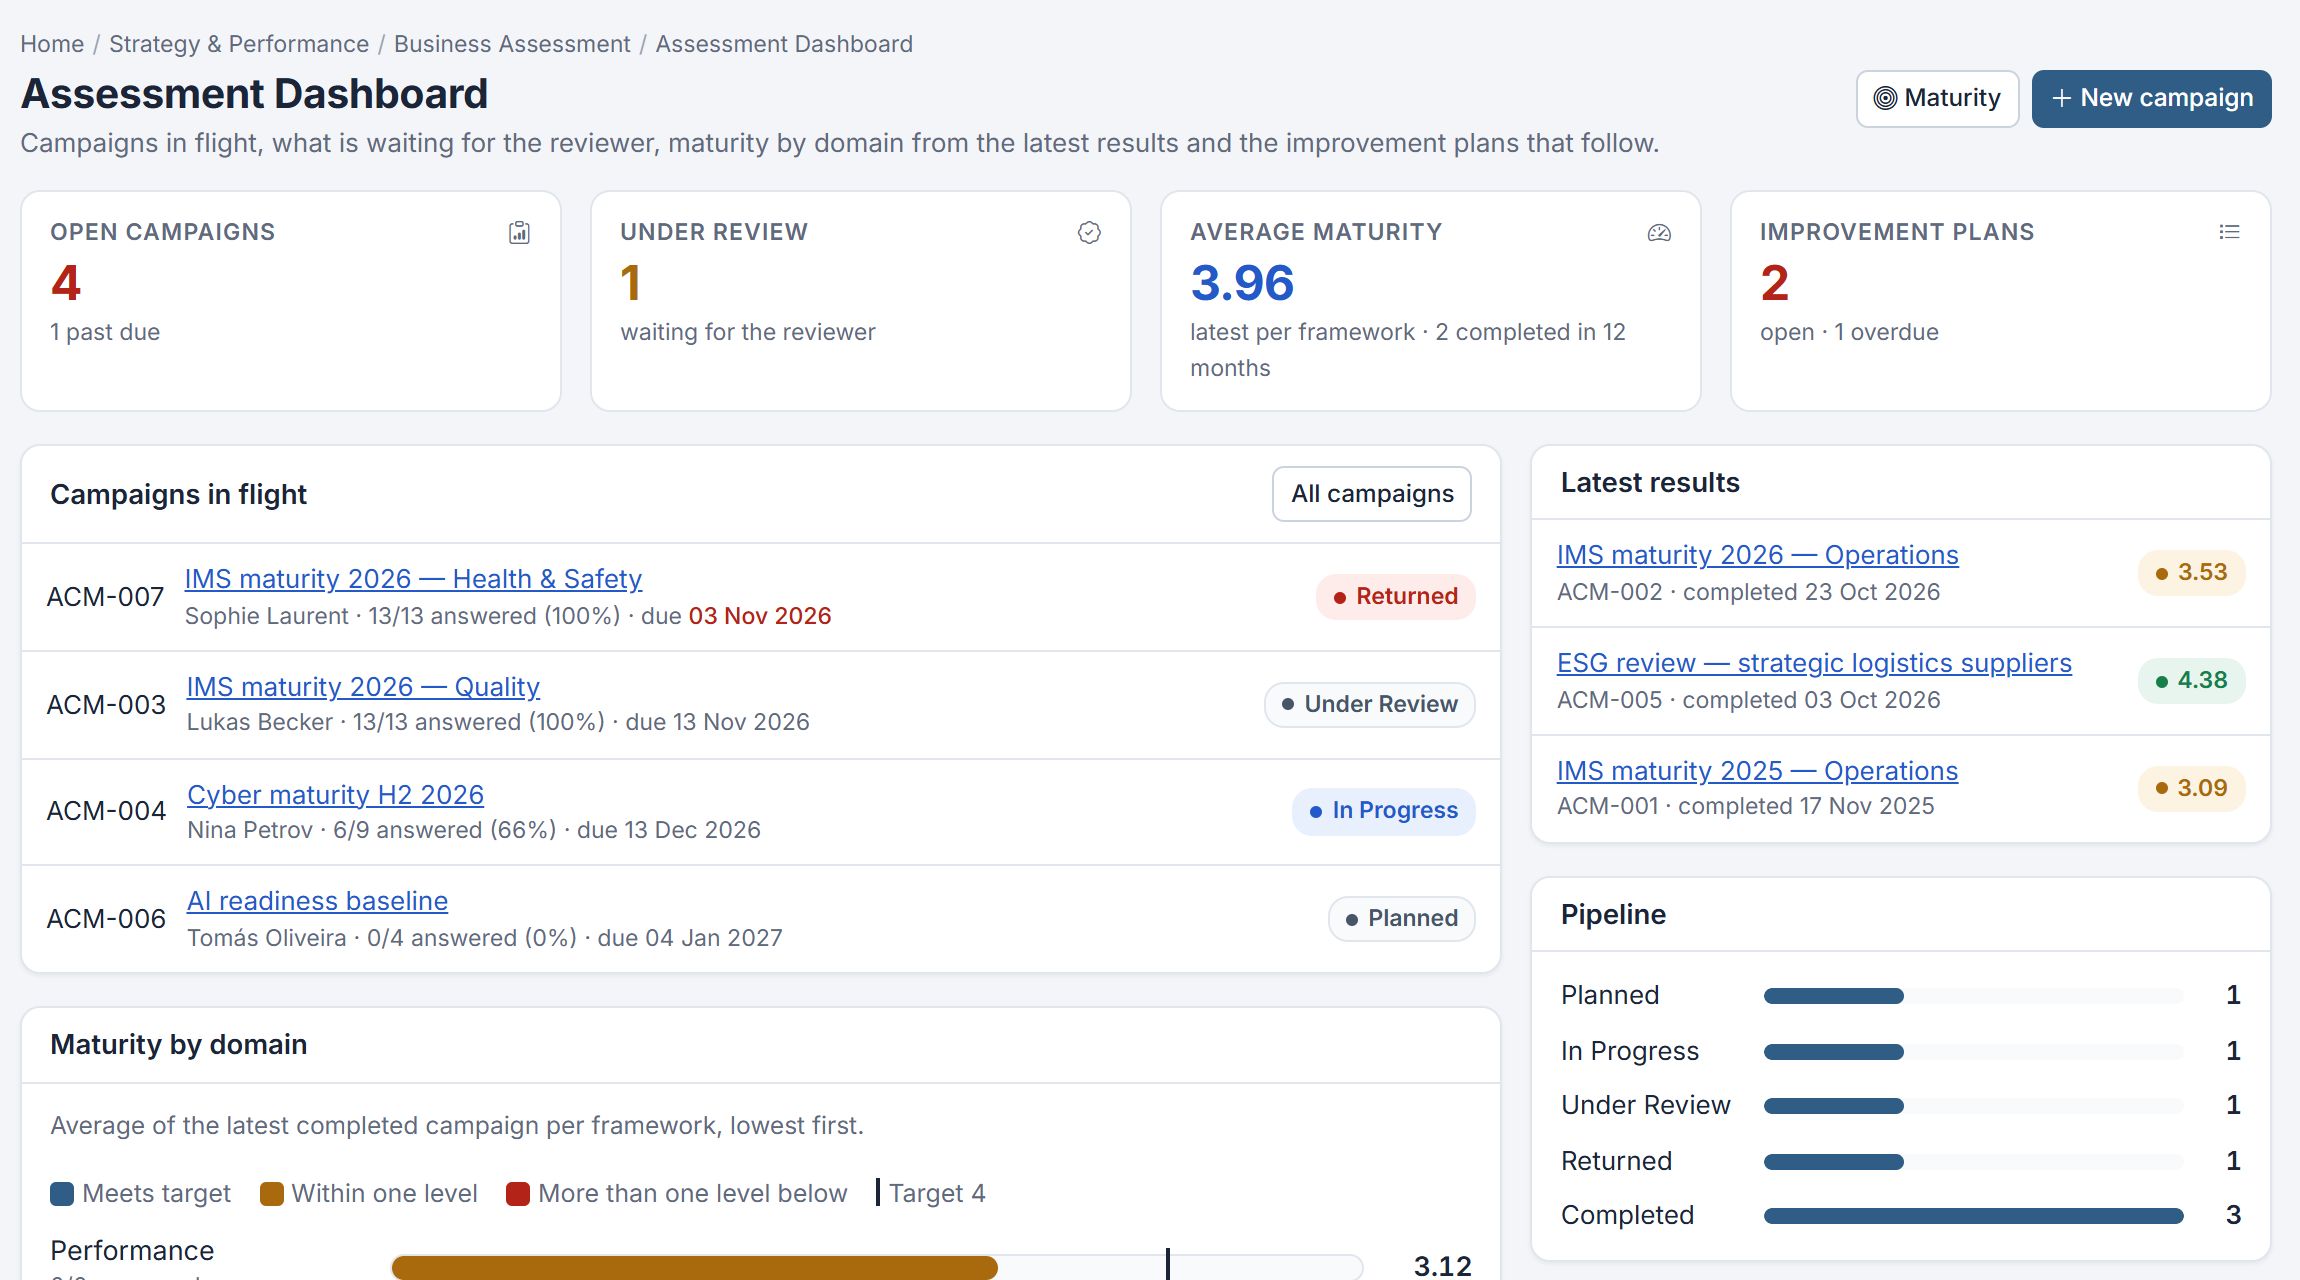
A maturity assessment is worth running only if it drives an improvement plan.
How to run a maturity assessment and gap analysis: questionnaires by domain, scoring against target maturity and improvement plans that close the gaps.
Articles on document control, audits, corrective action, risk, compliance, training and the other disciplines of ISO compliance and quality management.
Built for practitioners
No generic management theory. Each article focuses on the records, controls, workflows and evidence that quality, compliance and audit teams handle in practice.
58 articles
Business Assessment
How to run a maturity assessment and gap analysis: questionnaires by domain, scoring against target maturity and improvement plans that close the gaps.
Internal Audit
How to write clear internal audit findings, agree management responses and follow actions through to validated closure, in line with ISO 9001 and ISO 19011.
Organisation
How to meet ISO clause 4 in practice: internal and external issues, interested parties and their requirements, and a management system scope that stays current.
Customer Engagement
How to monitor customer satisfaction for ISO 9001 clause 9.1.2 with surveys, NPS and CSAT, account health and complaints, and turn results into improvement.
Document Control
What ISO 9001 clause 7.5 actually asks of documented information, and how document control software keeps one approved revision in force, read and retained.
Event Management
How to plan workshops, conferences and supplier days with quality controls: readiness checks, agendas, capacity-controlled registration, check-in and records.
Risk Management
How to score inherent and residual risk, define risk appetite, use a heatmap and record risk acceptance so the register supports real decisions.
Process Management
How to manage process changes with change requests: impact assessment, approval, implementation and updated process maps, in line with ISO 9001 6.3 and 8.5.6.
Strategy & Objectives
How to set quality objectives that meet ISO 9001 clause 6.2: consistent with policy, measurable, owned, resourced, monitored and reviewed through the year.
Supplier Management
How to meet ISO 9001 clause 8.4 with supplier evaluation criteria, selection, performance monitoring and re-evaluation proportionate to supplier criticality.
Strategy & Objectives
How to combine a balanced scorecard for multi-year strategy with OKRs for quarterly execution, using weighted objectives, strategy maps and initiatives.
Incident Management
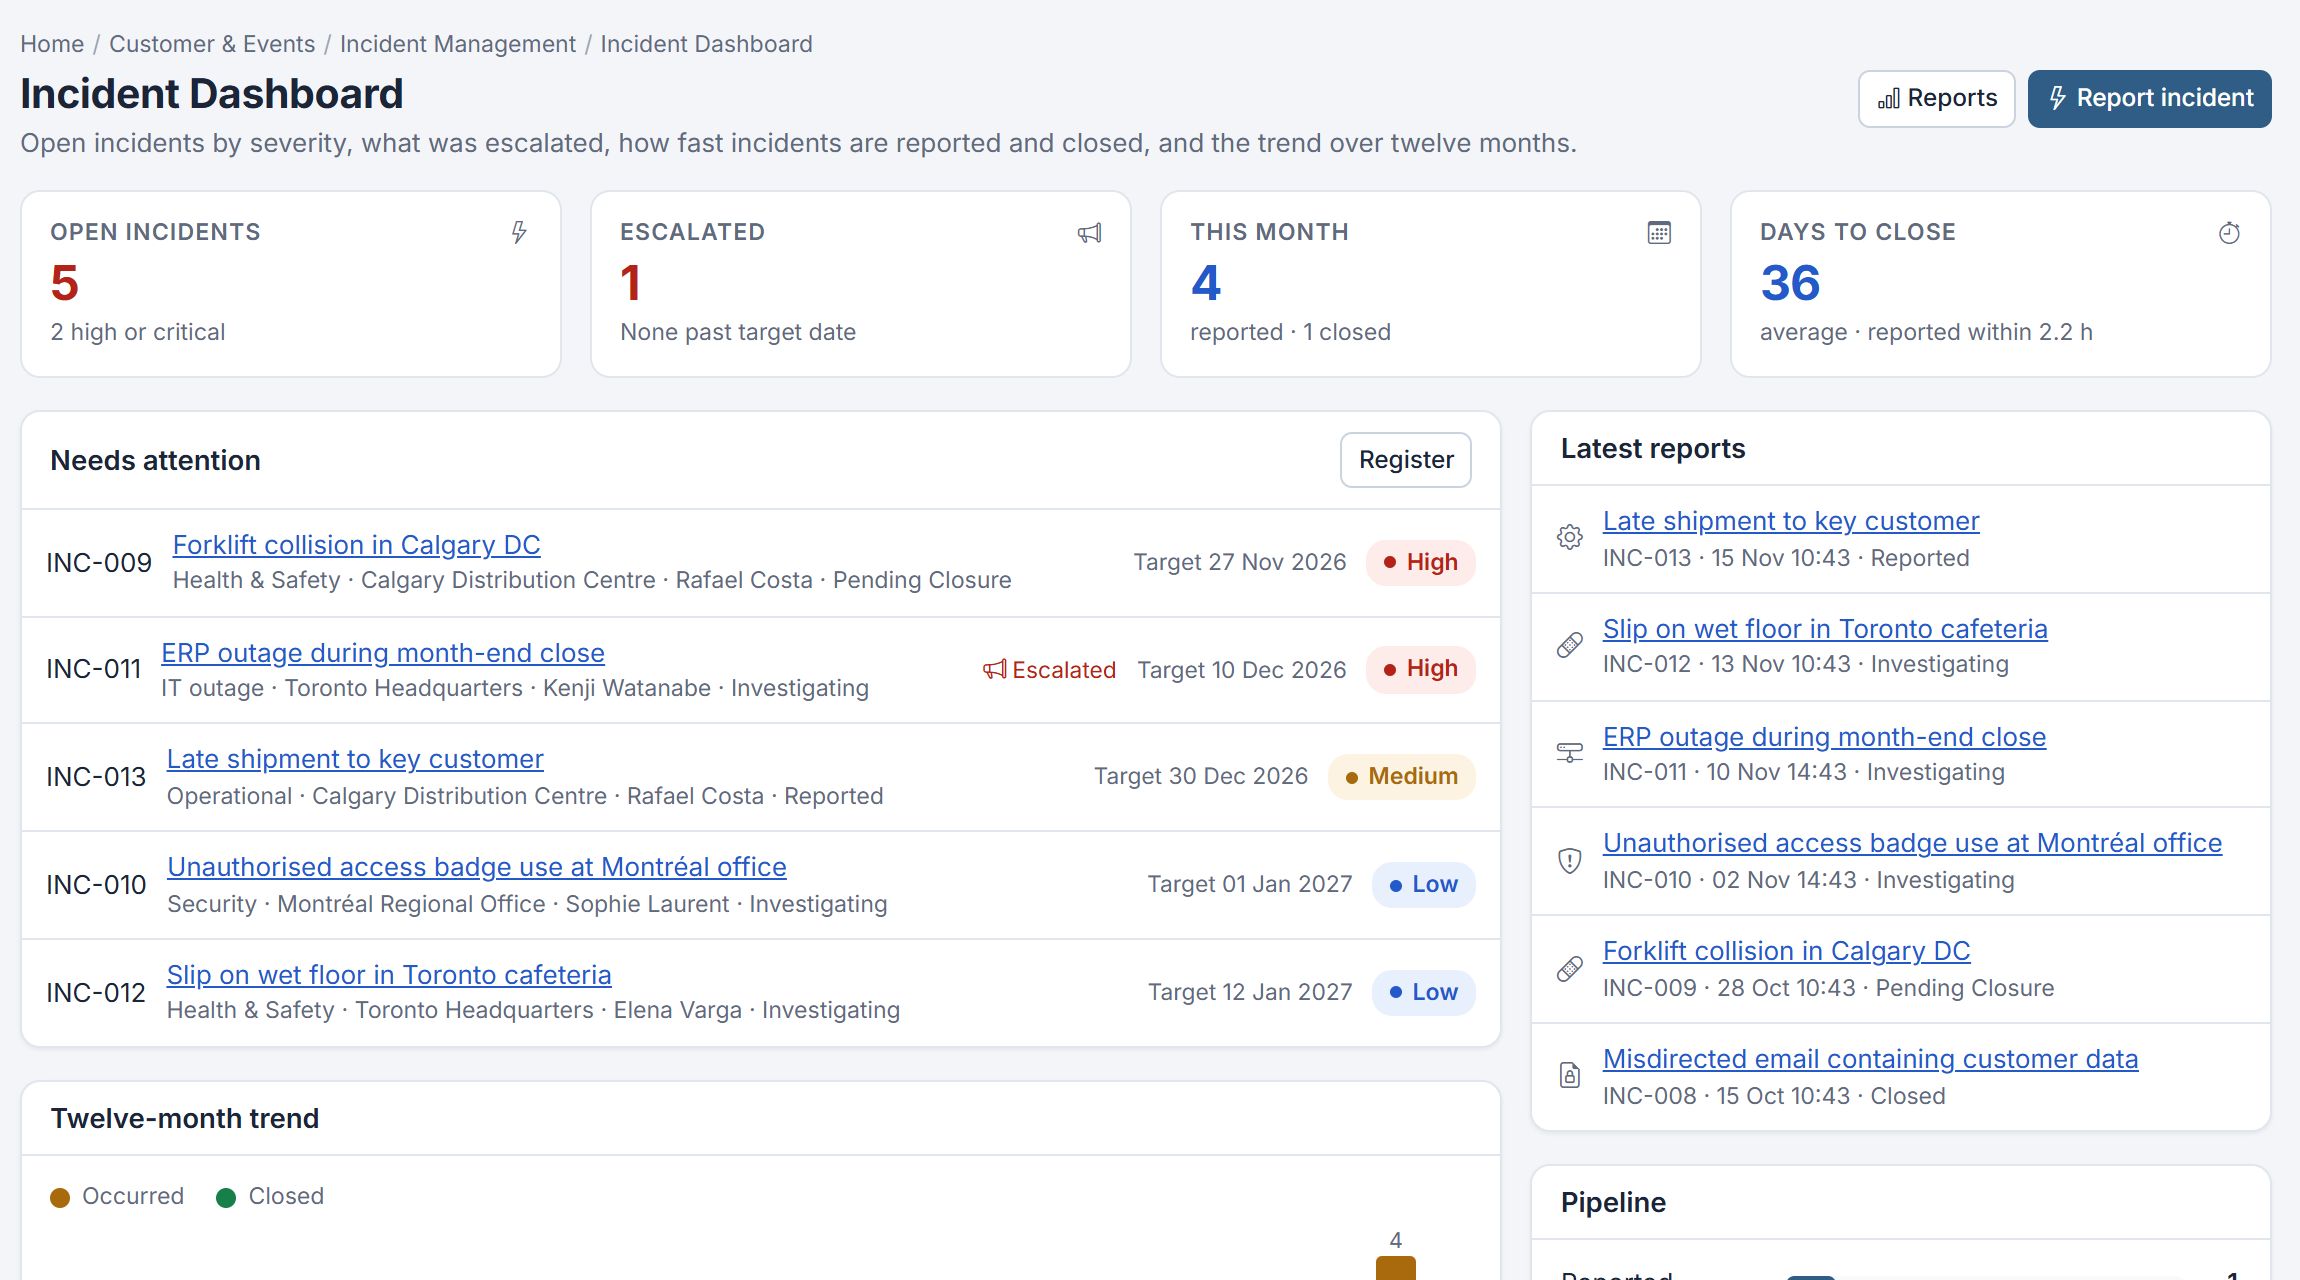
How to design incident reporting people actually use, then triage, investigate, assess impact and raise corrective actions in line with ISO 45001 and ISO 9001.
External Audit
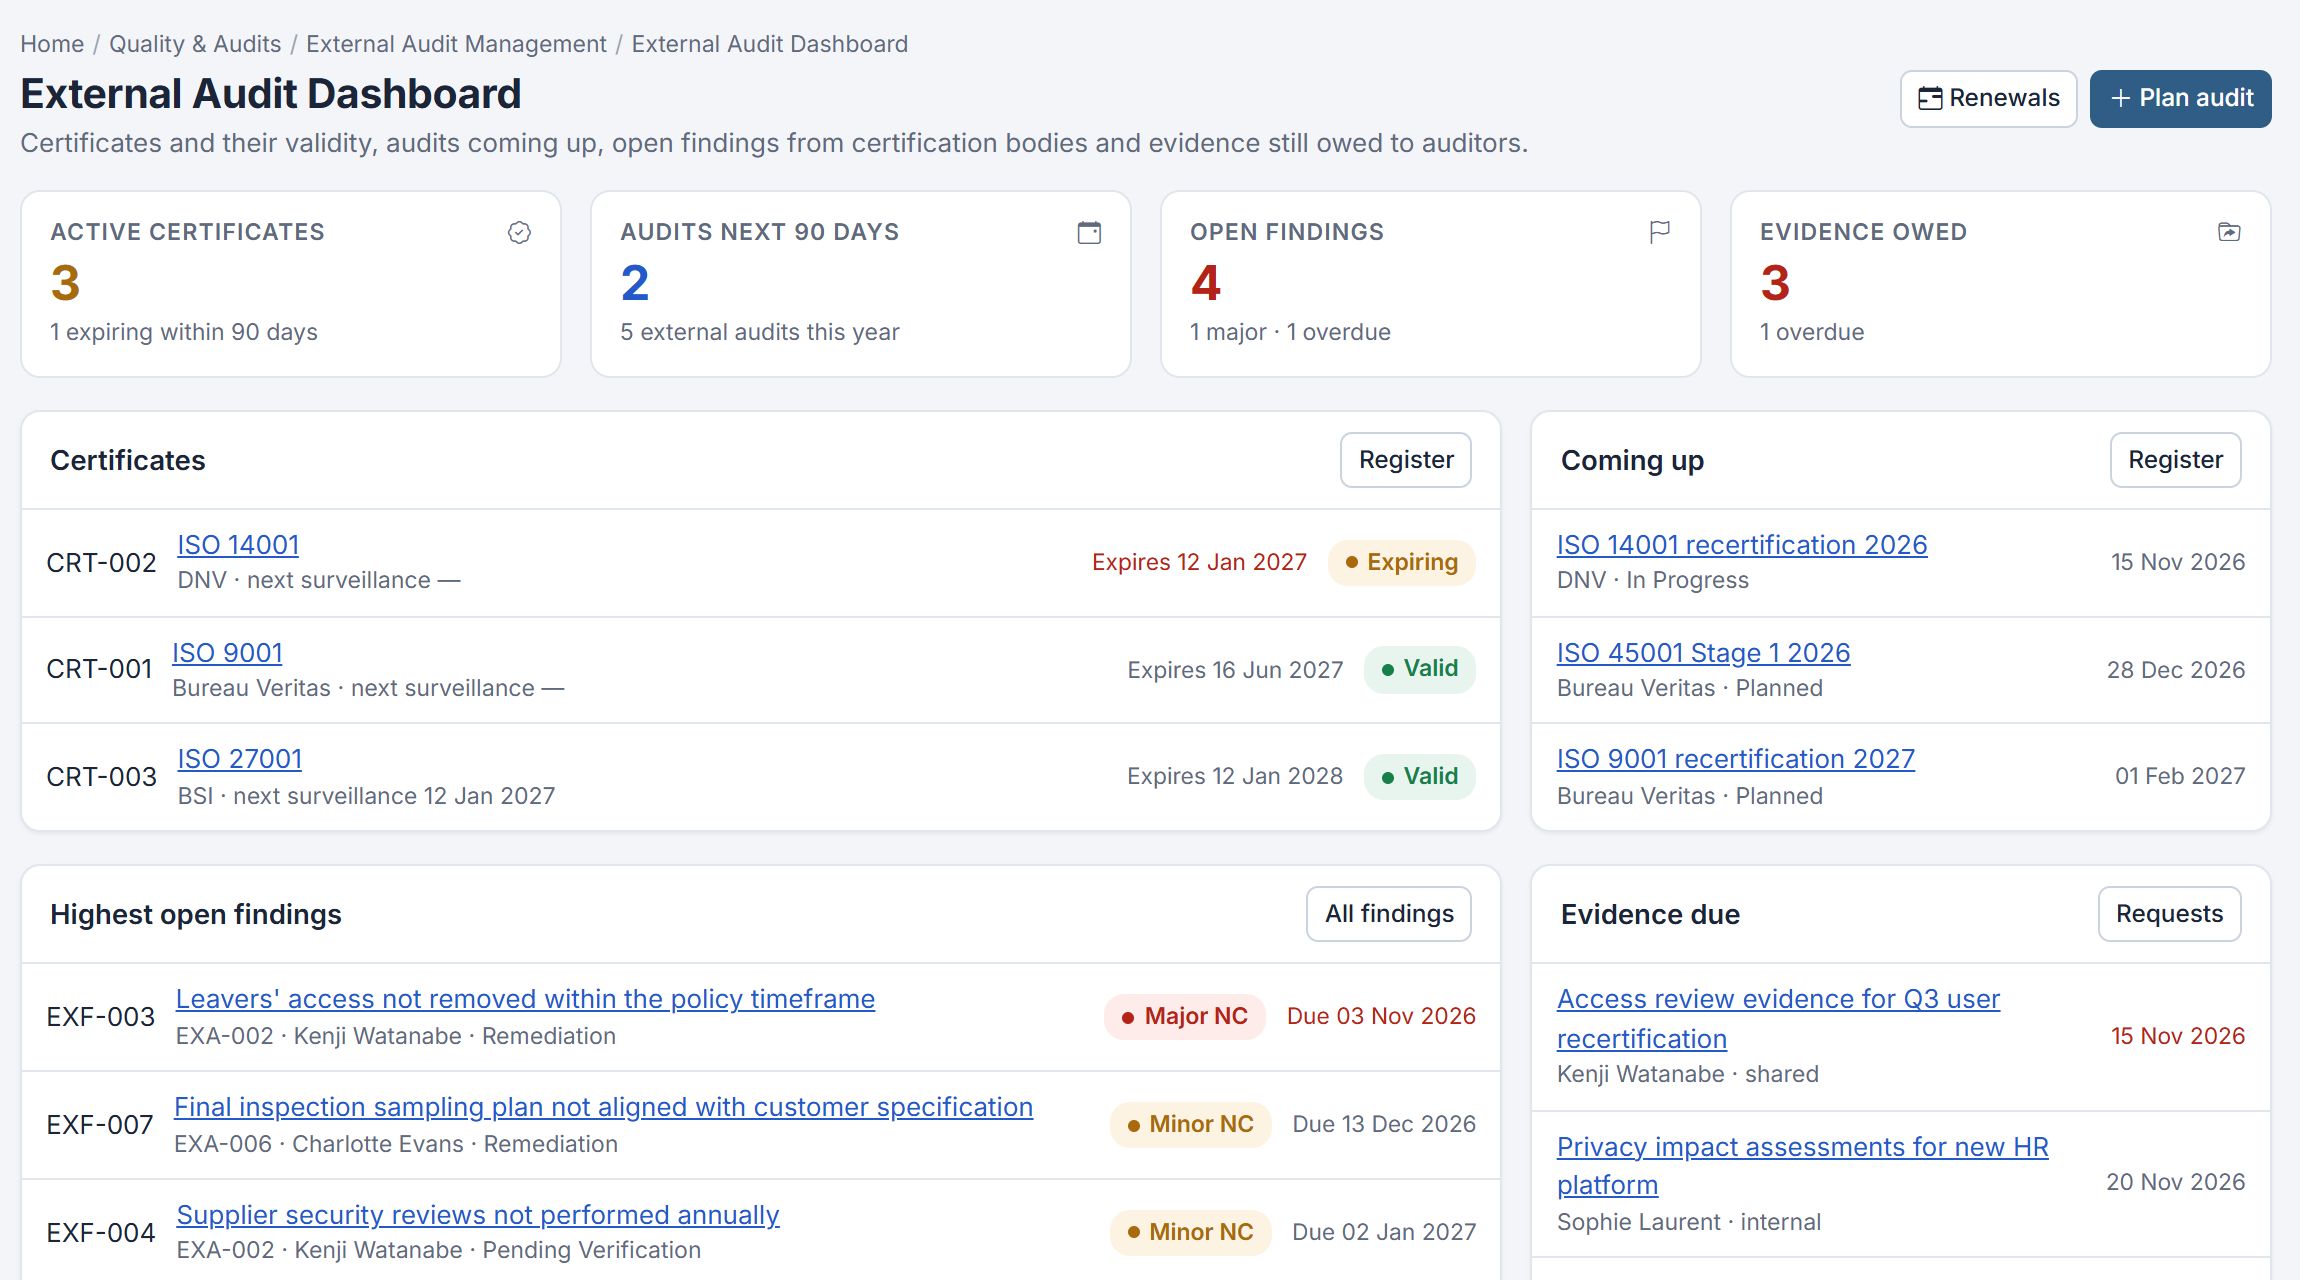
What happens in stage 1 and stage 2 of an ISO certification audit under ISO/IEC 17021-1, what auditors look for, and how to prepare your evidence.
Asset Management
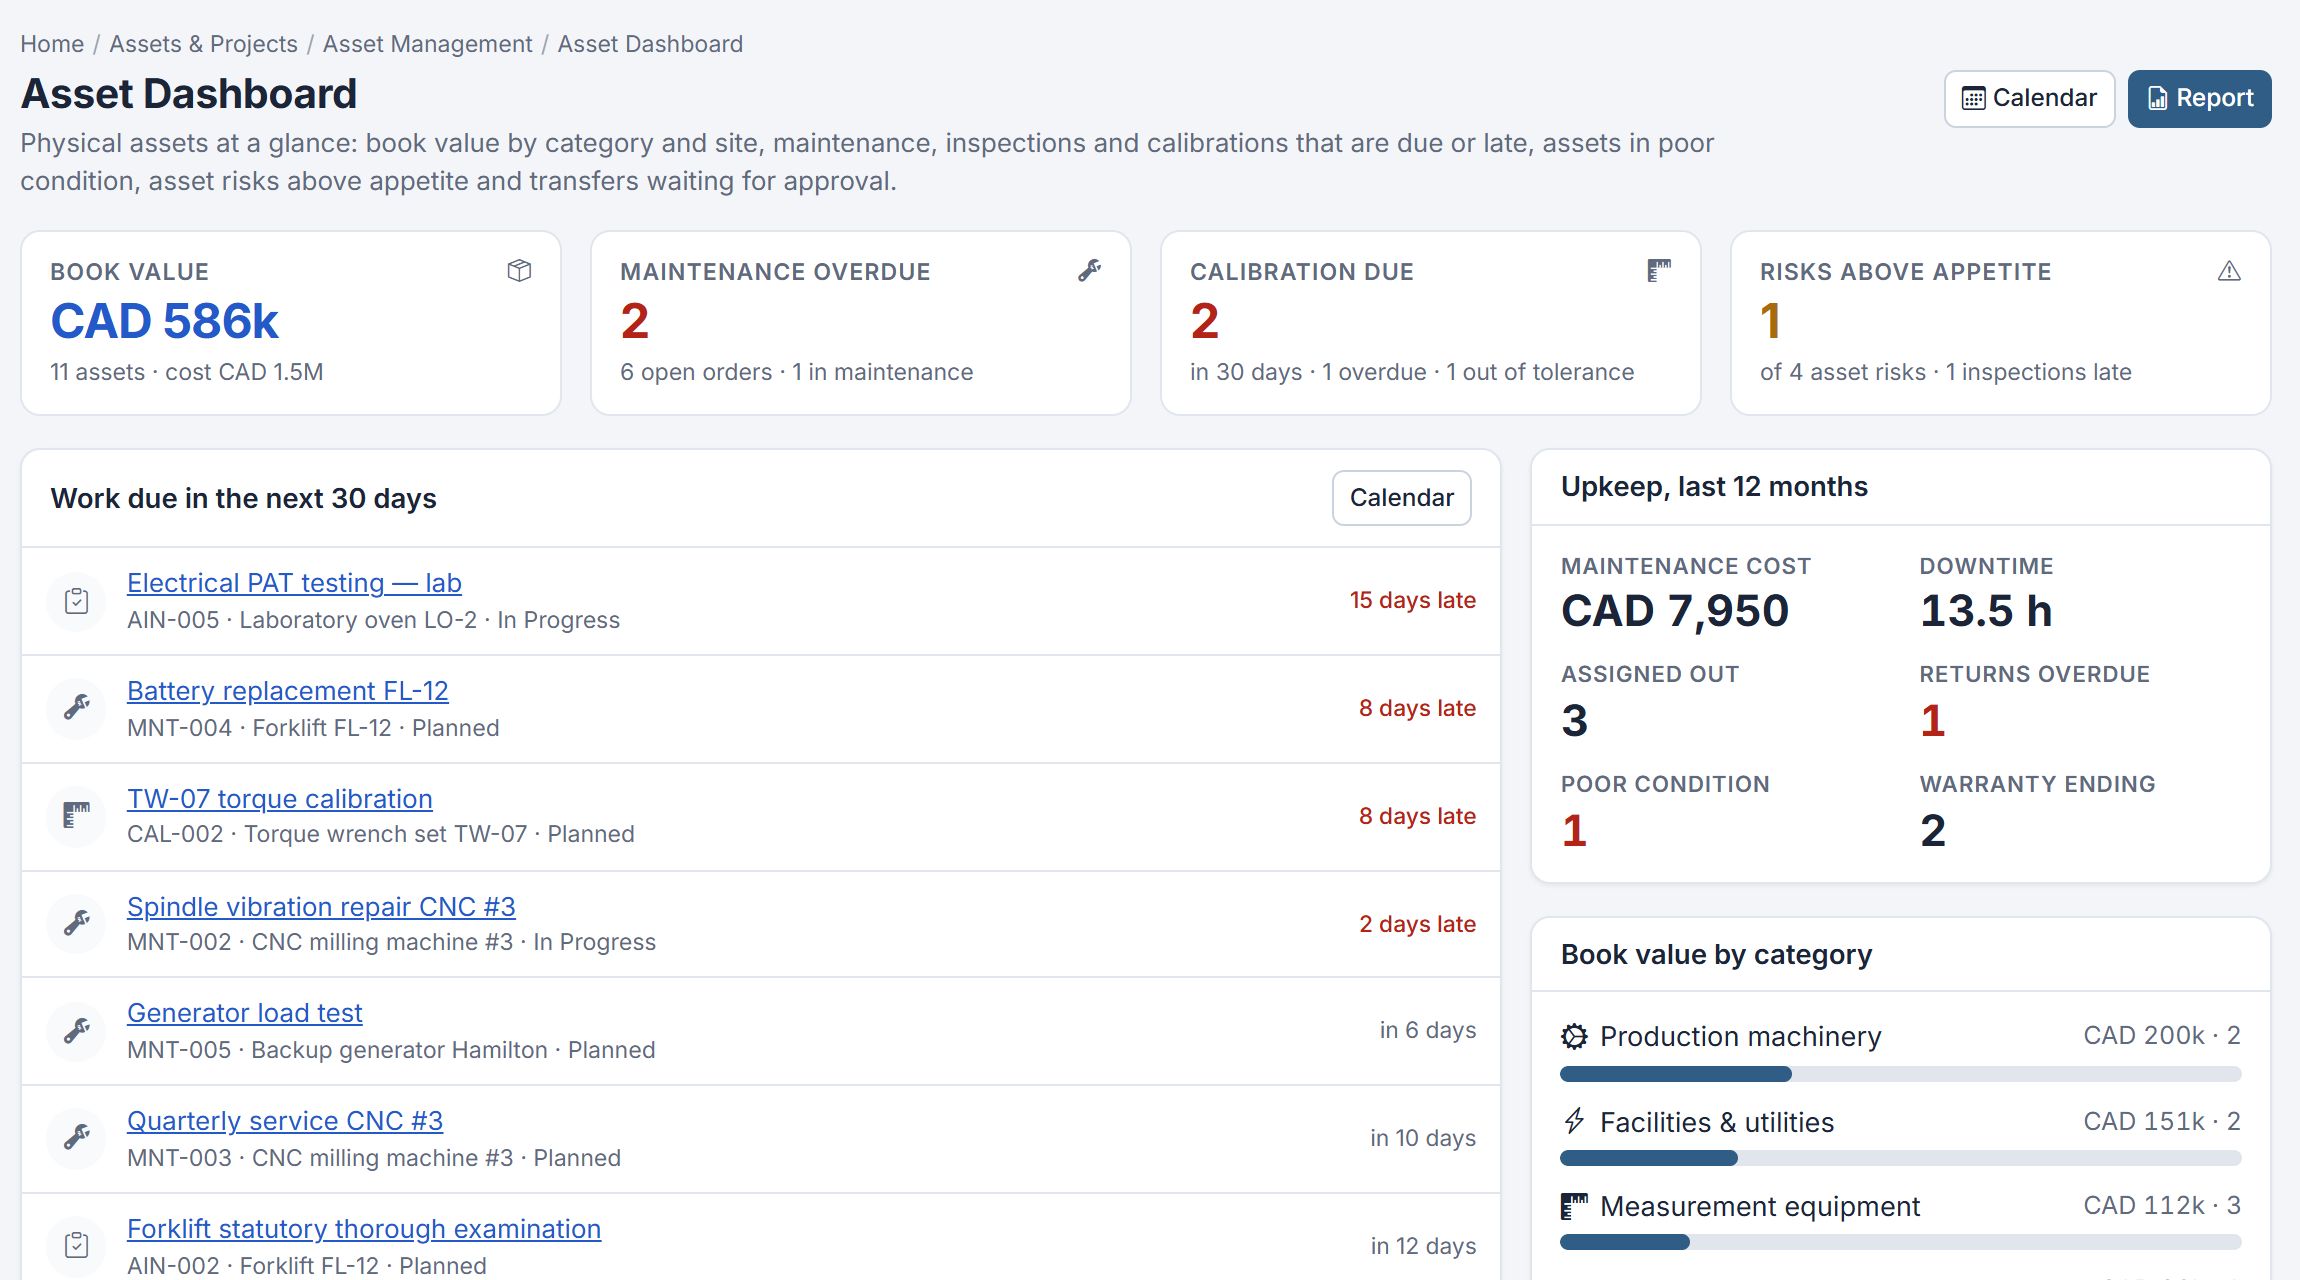
How an accurate asset register supports preventive maintenance, inspections, custody, transfers and disposals, in line with ISO 9001 and ISO 55001.
Business Assessment
How to make self-assessments reliable: evidence-based answers, independent validation, clear scoring rules and an audit trail from answer to score.
Information Security
How to run user access review campaigns for ISO/IEC 27001: scope, reviewers, certify-or-revoke decisions, evidence of removal and audit-ready results.
Cybersecurity
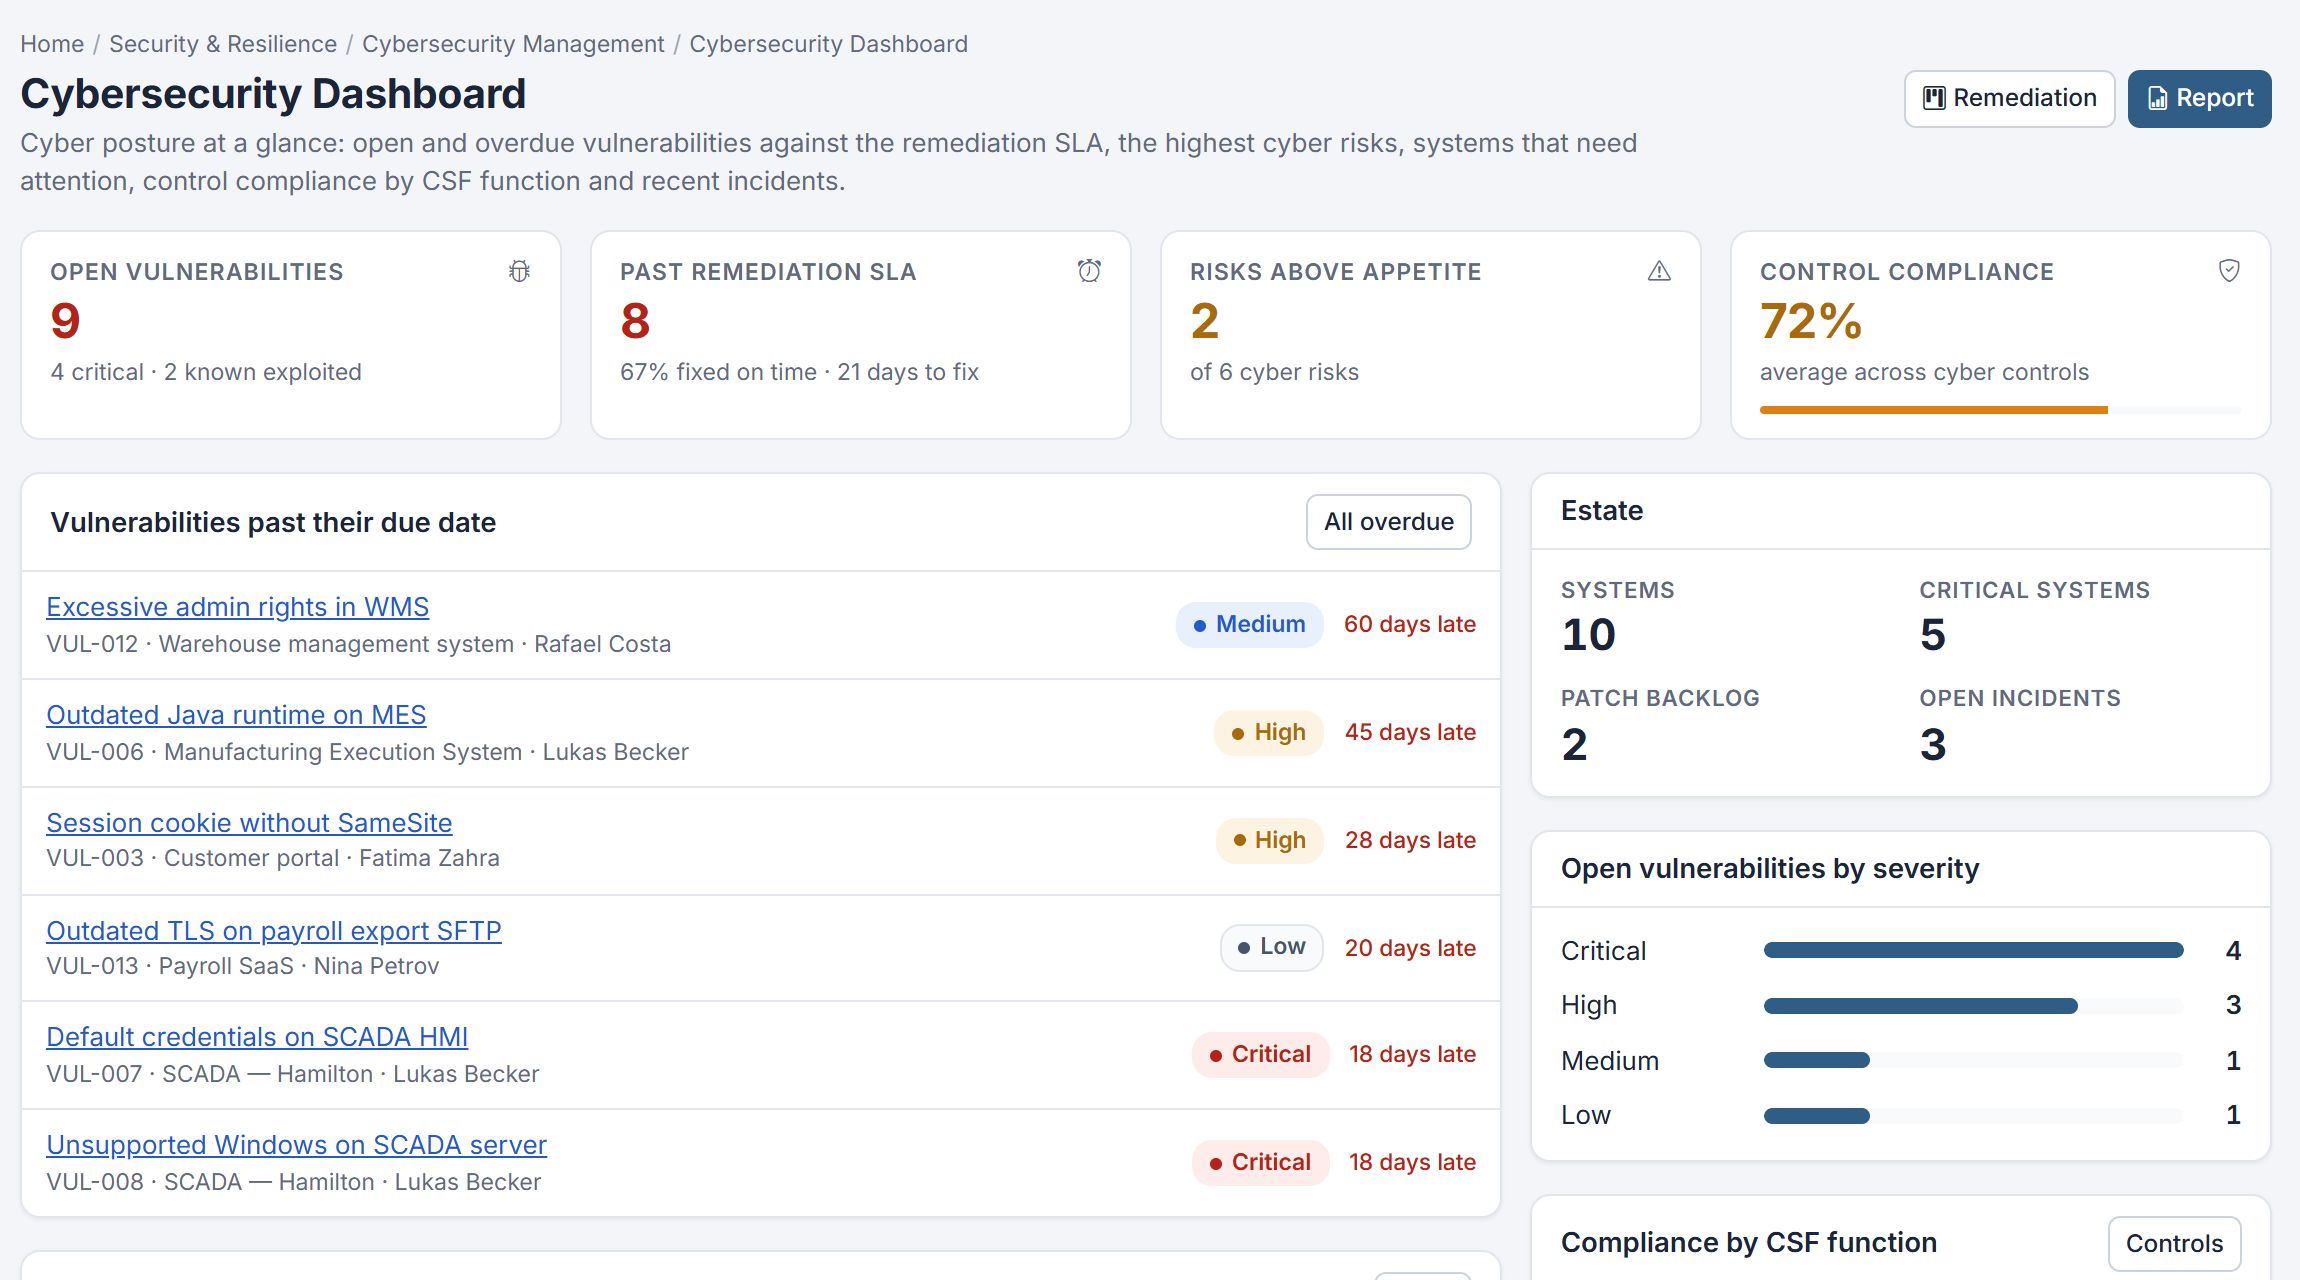
How to run vulnerability management with severity-based remediation SLAs, a system inventory, tracked exceptions and reporting, aligned with ISO/IEC 27001.
Compliance Management
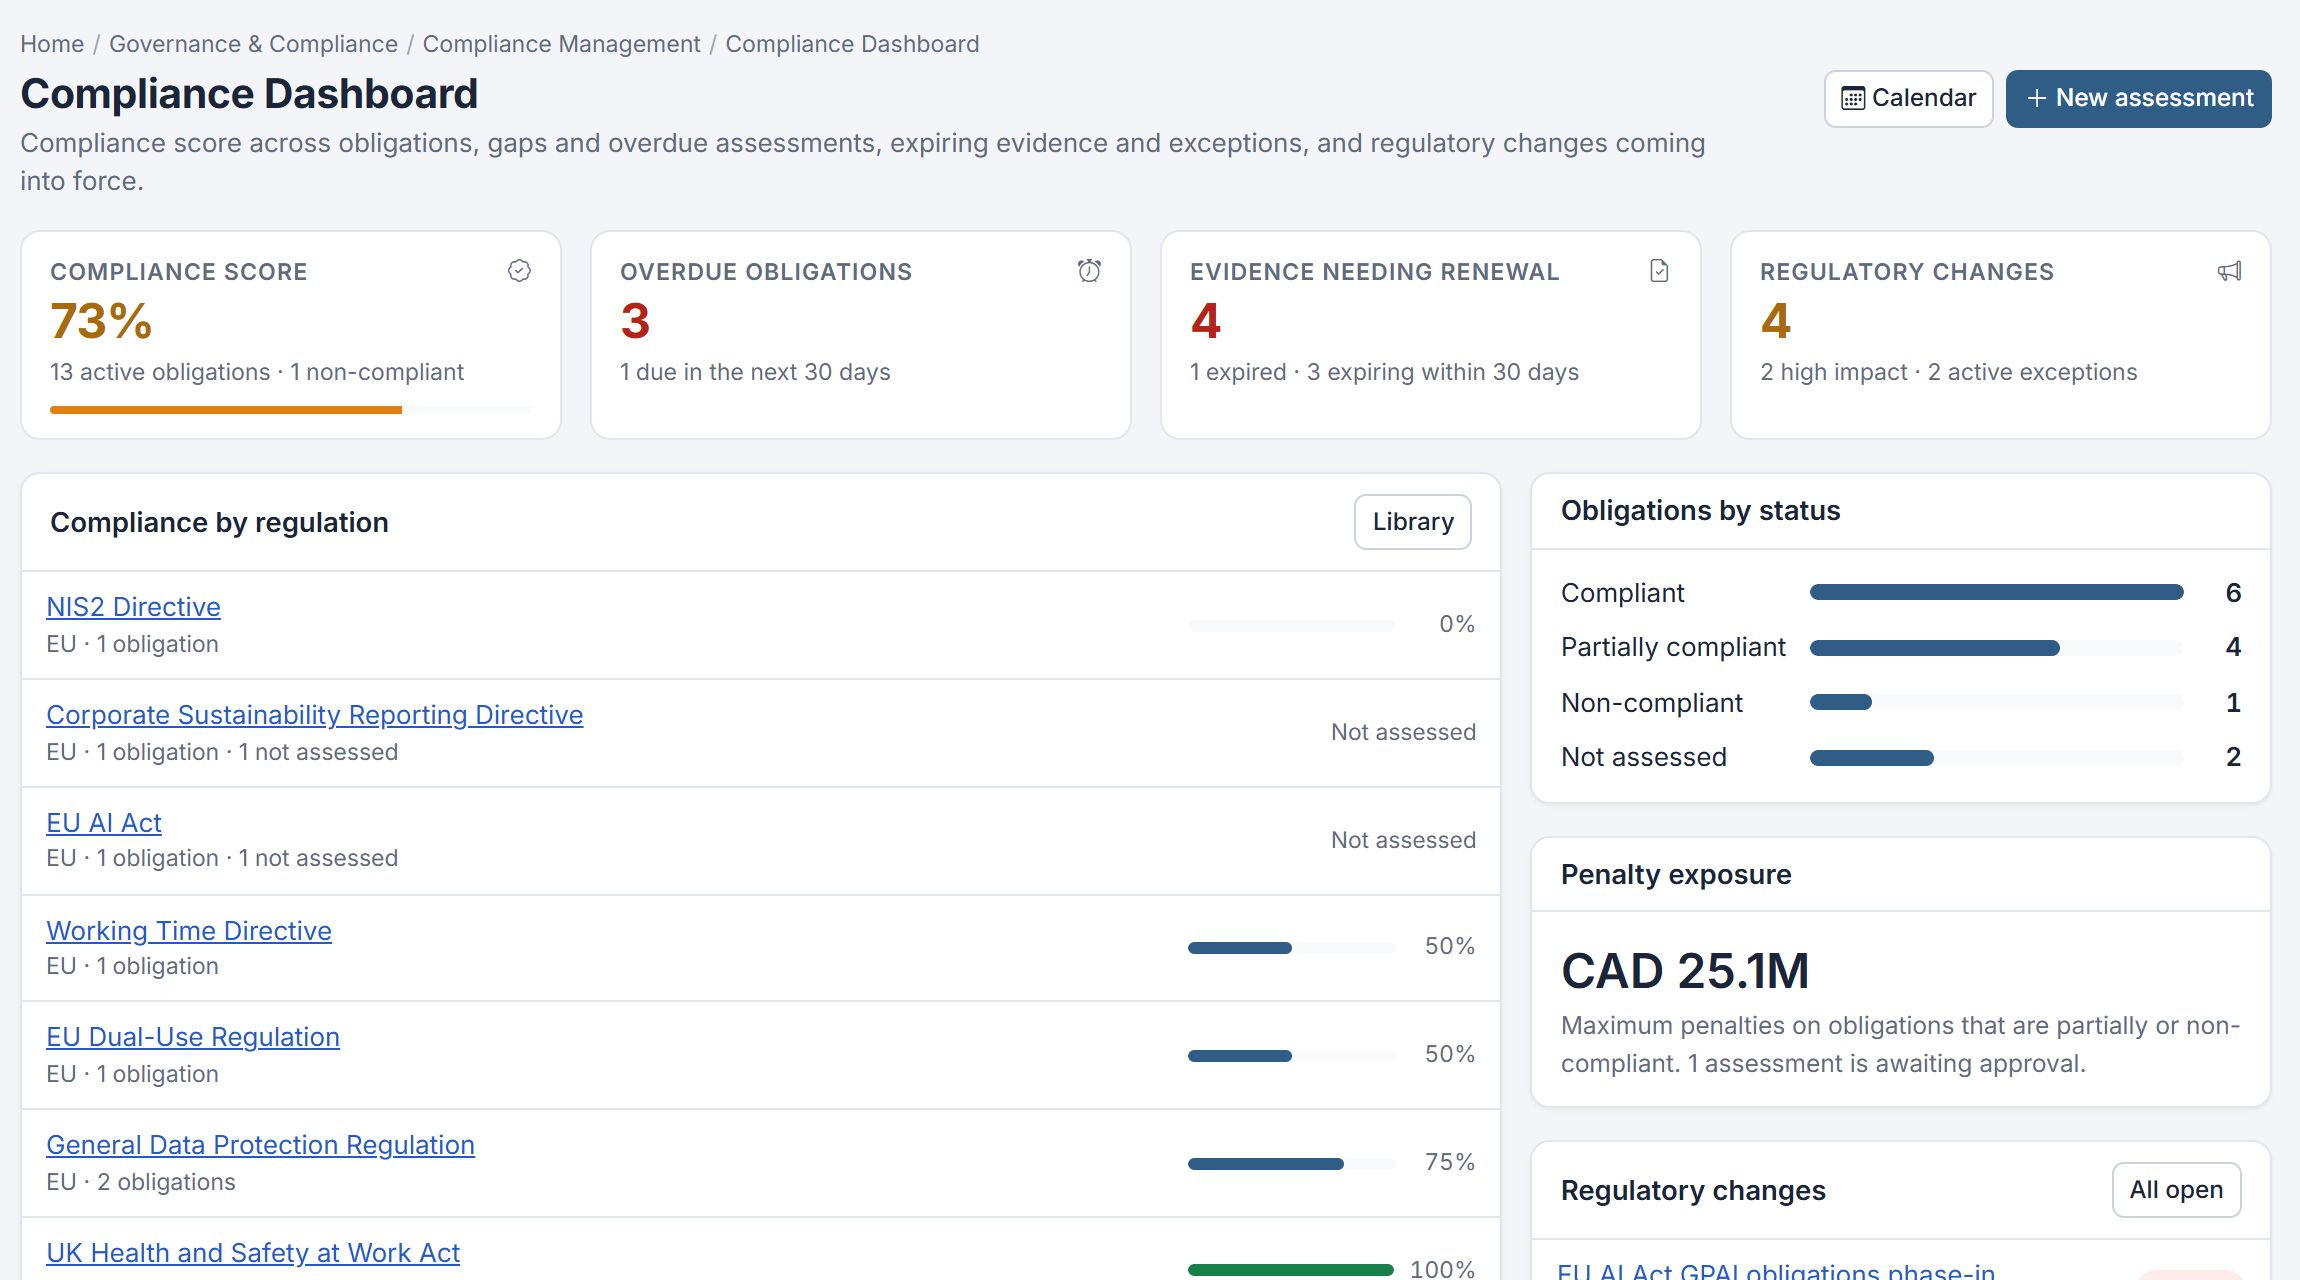
How to build a compliance obligations register that stays current: sources, owned obligations, scheduled assessments, evidence and exceptions.
Governance & Controls
How to design and maintain a delegation of authority matrix: decision types, limits by role, sub-delegation, review cycles and evidence for auditors.
Training Management
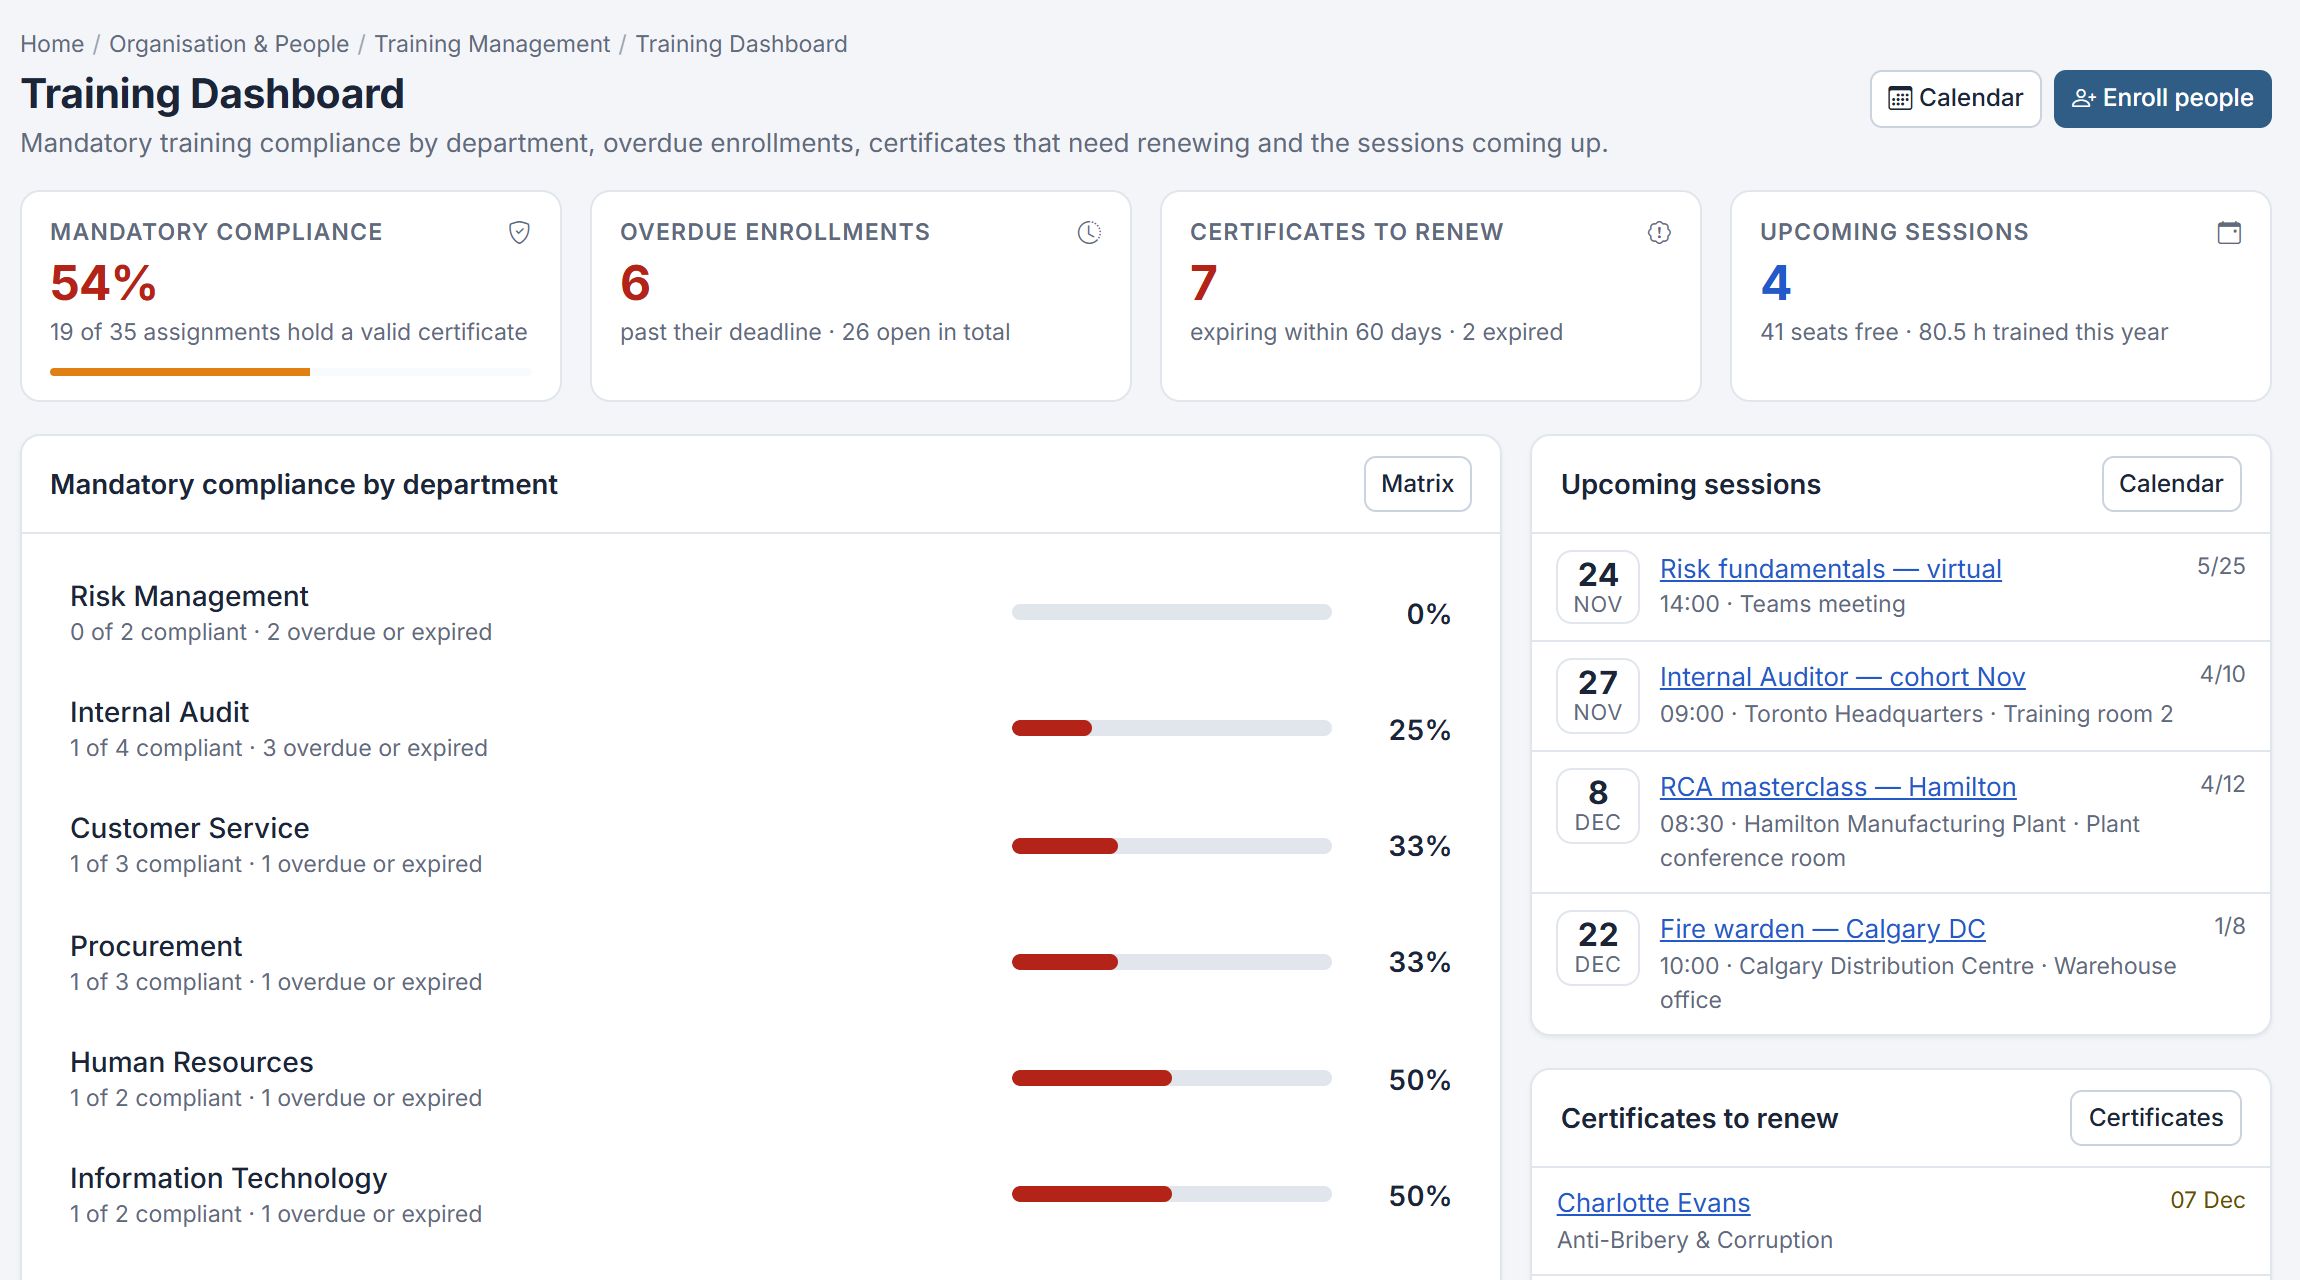
How a training matrix keeps mandatory training current across departments, with plans, enrolments, certificates and expiry tracking that support ISO audits.
Nonconformity & CAPA
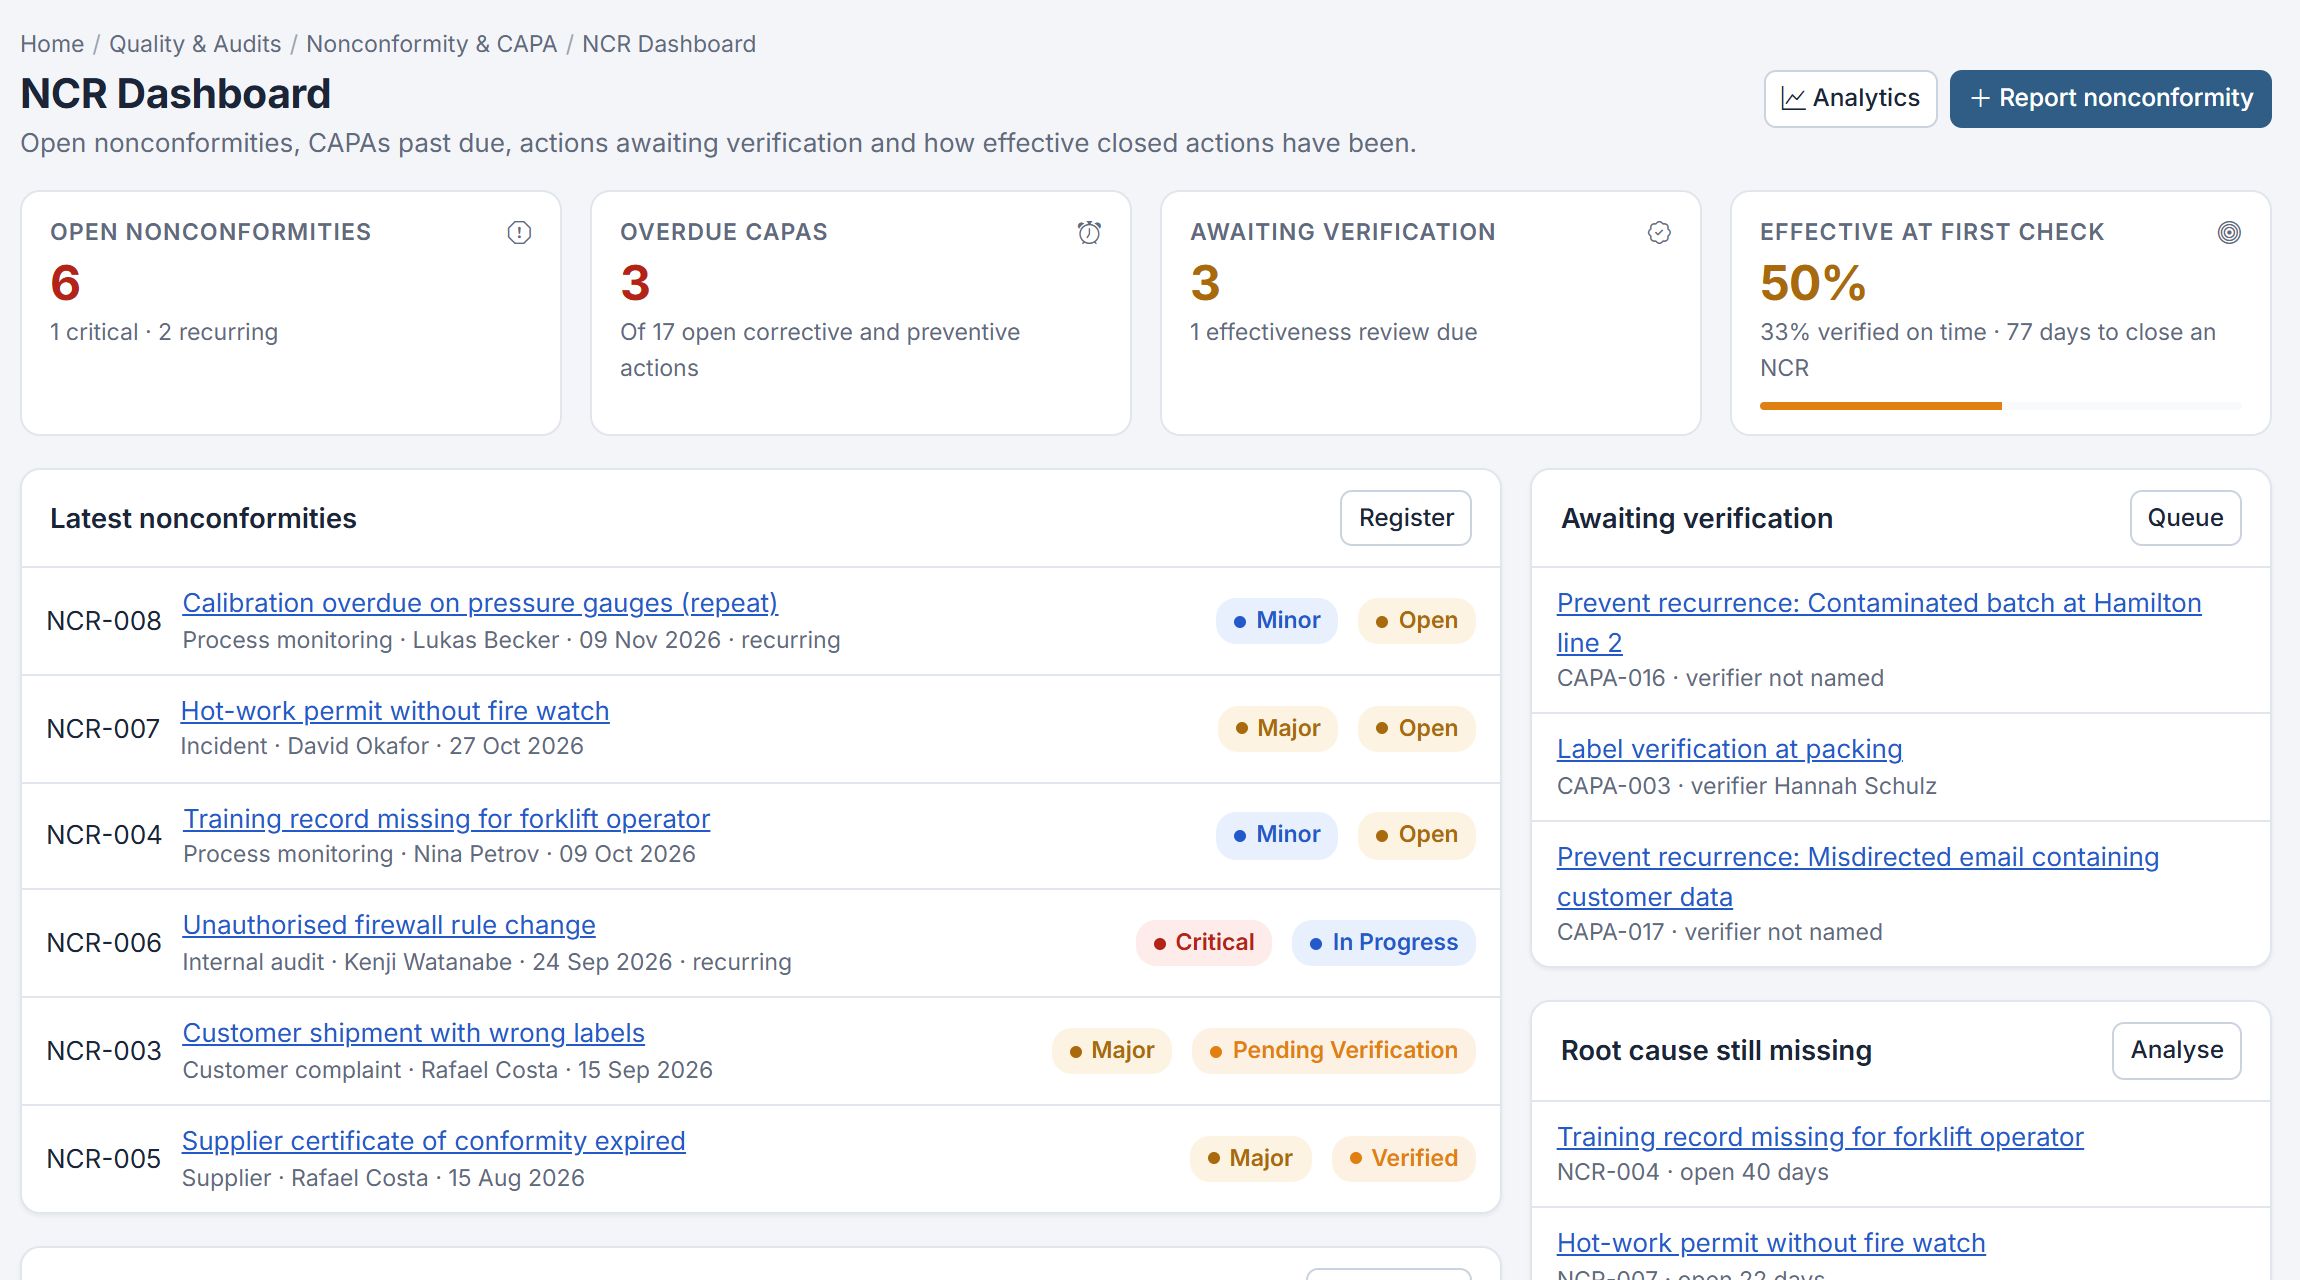
Why ISO 9001 asks you to review corrective action effectiveness, how to set criteria before closure, and why a 90-day check catches recurrence.
External Audit
How the three-year ISO certification cycle works, what surveillance and recertification audits cover, and how to track certificates and renewal dates.
AI Governance
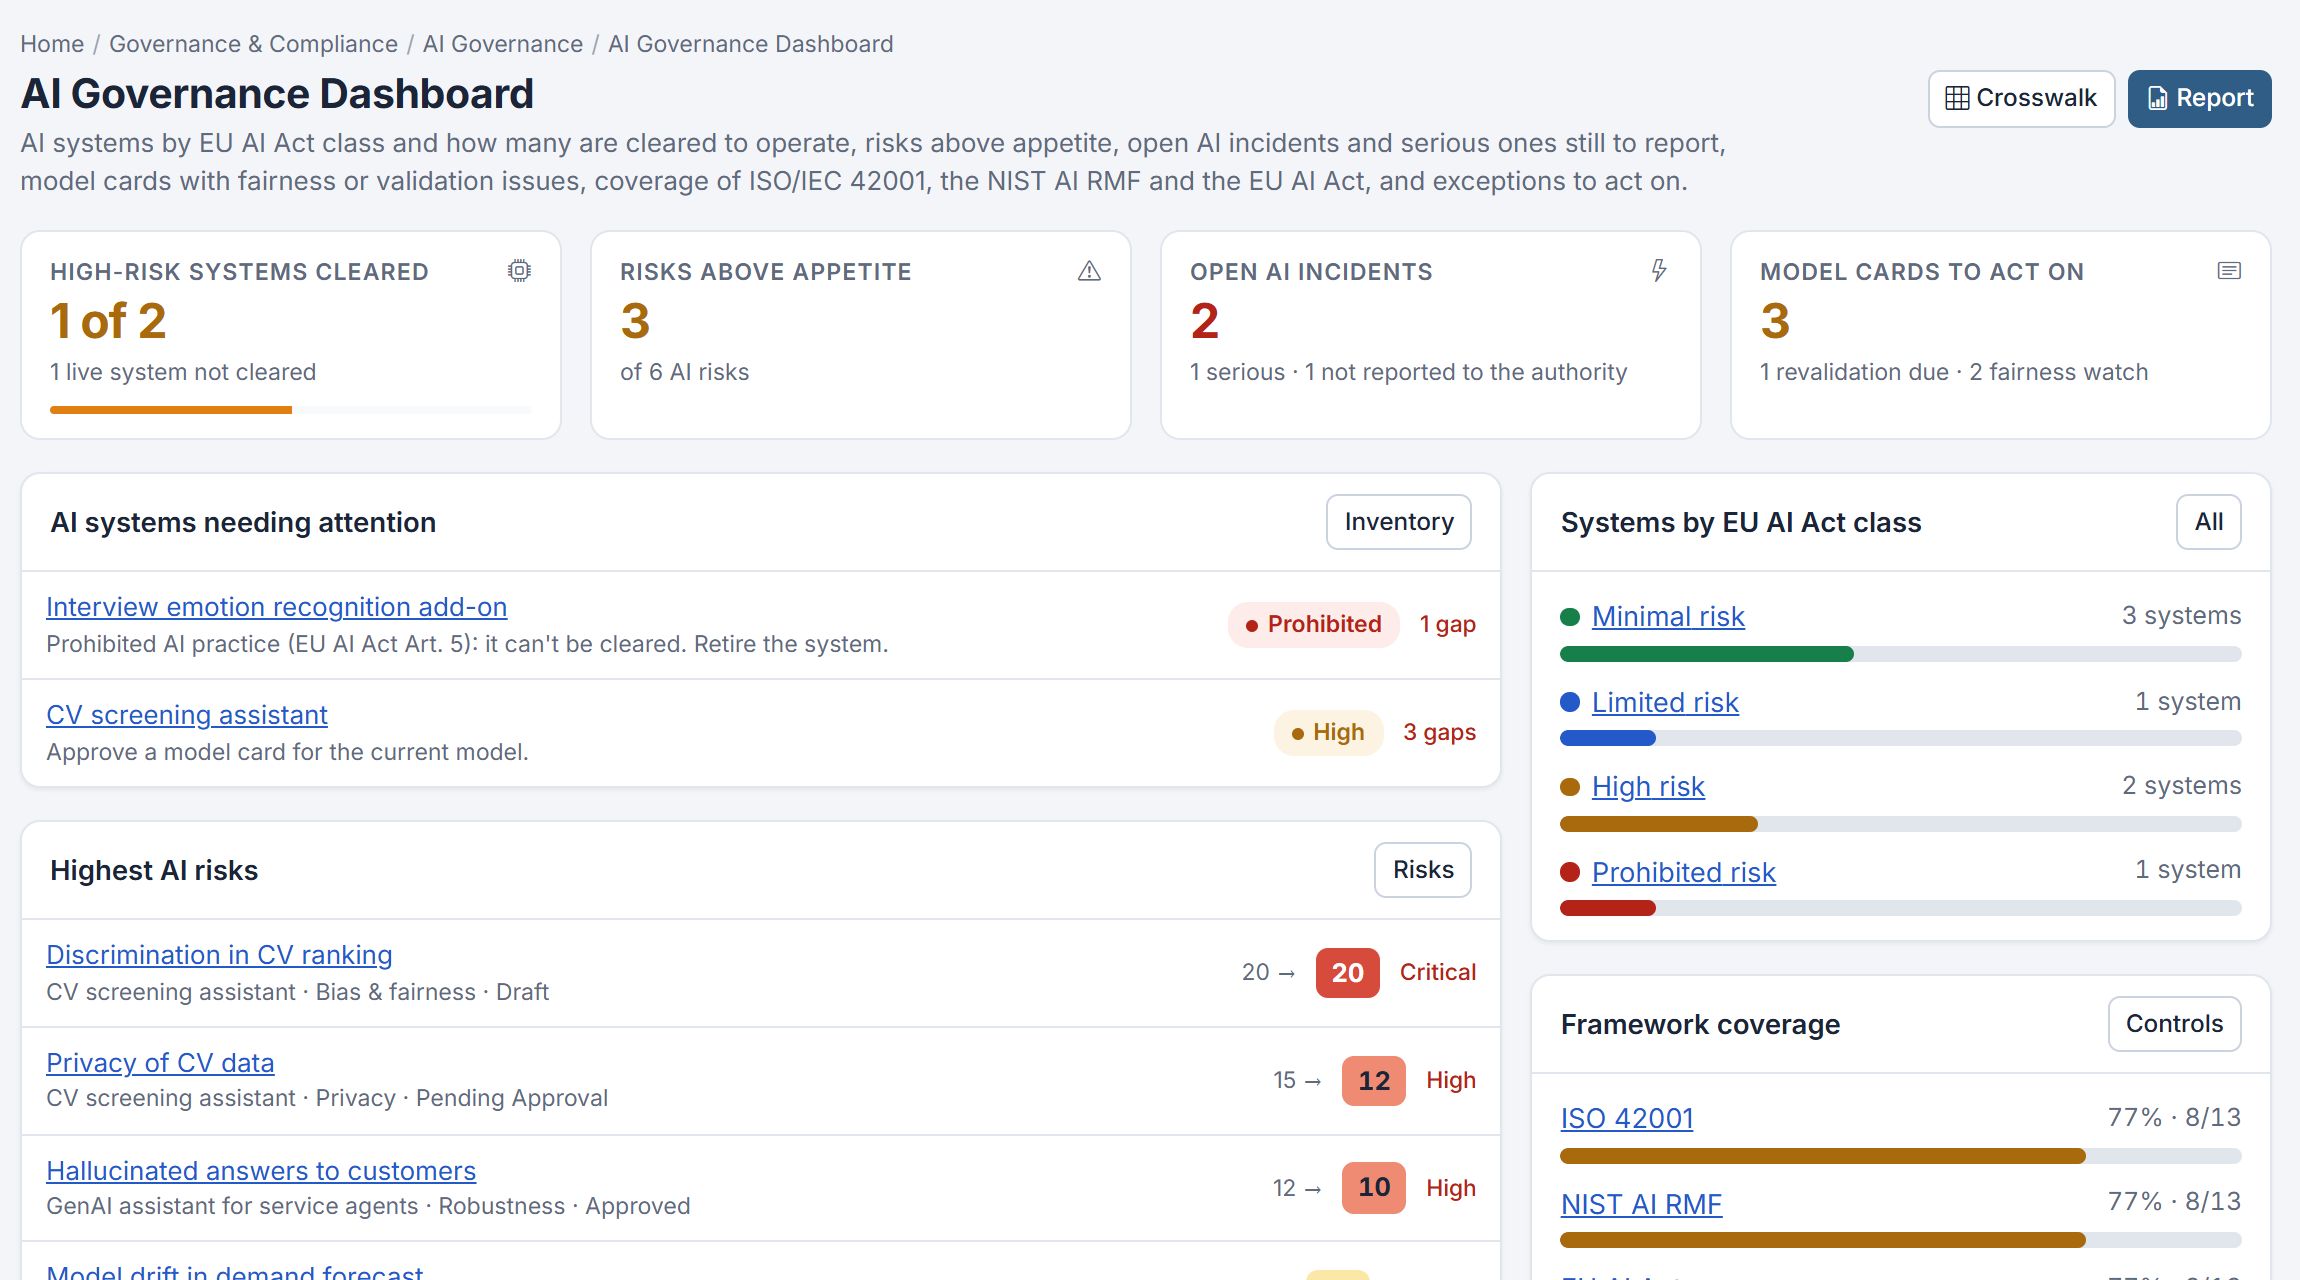
How model cards with fairness and validation gates, and structured AI risk assessments, support AI clearance decisions under ISO/IEC 42001 and the EU AI Act.
Knowledge Hub
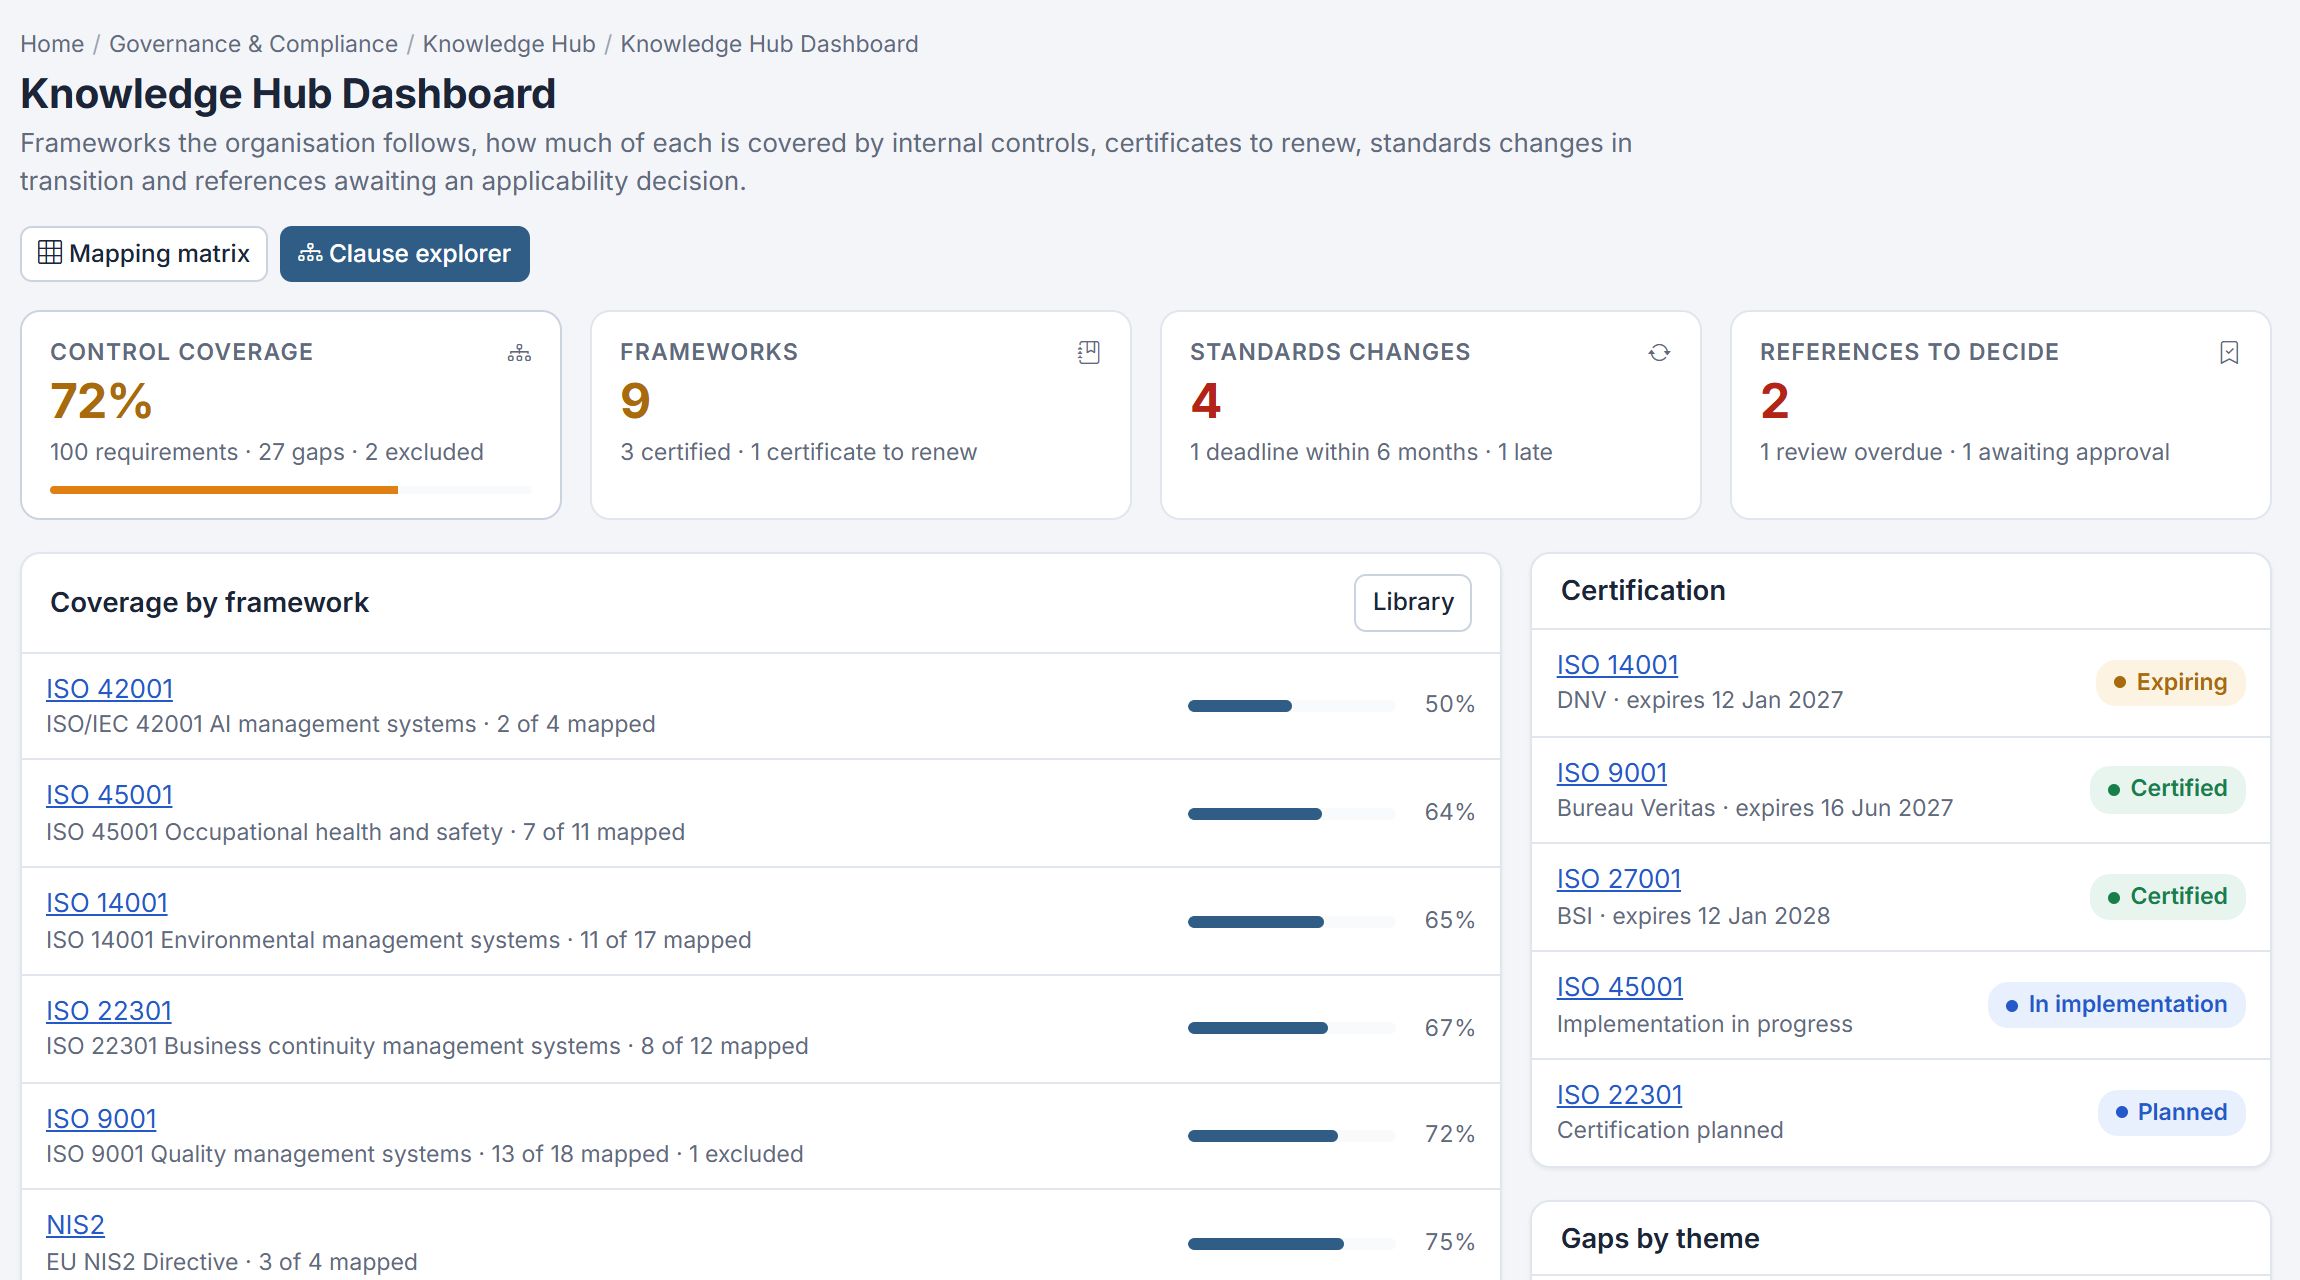
How to run an integrated management system across ISO 9001, ISO 14001, ISO 45001 and ISO 27001 by mapping one set of controls to many requirements.
KPI Management
How to define quality KPIs for ISO 9001 clause 9.1 with formulas, targets and thresholds, approved periodic results and an audit trail for target changes.
Document Control
How read-and-understood acknowledgements turn document publication into audit evidence that the right people know the current procedure.
Organisation
How to meet ISO clause 5.3 by assigning and communicating roles, responsibilities and authorities through positions, reporting lines and process ownership.
Event Management
How to collect event feedback with ratings, write a post-event summary and raise an improvement action when an event falls below expectations.
Management Review
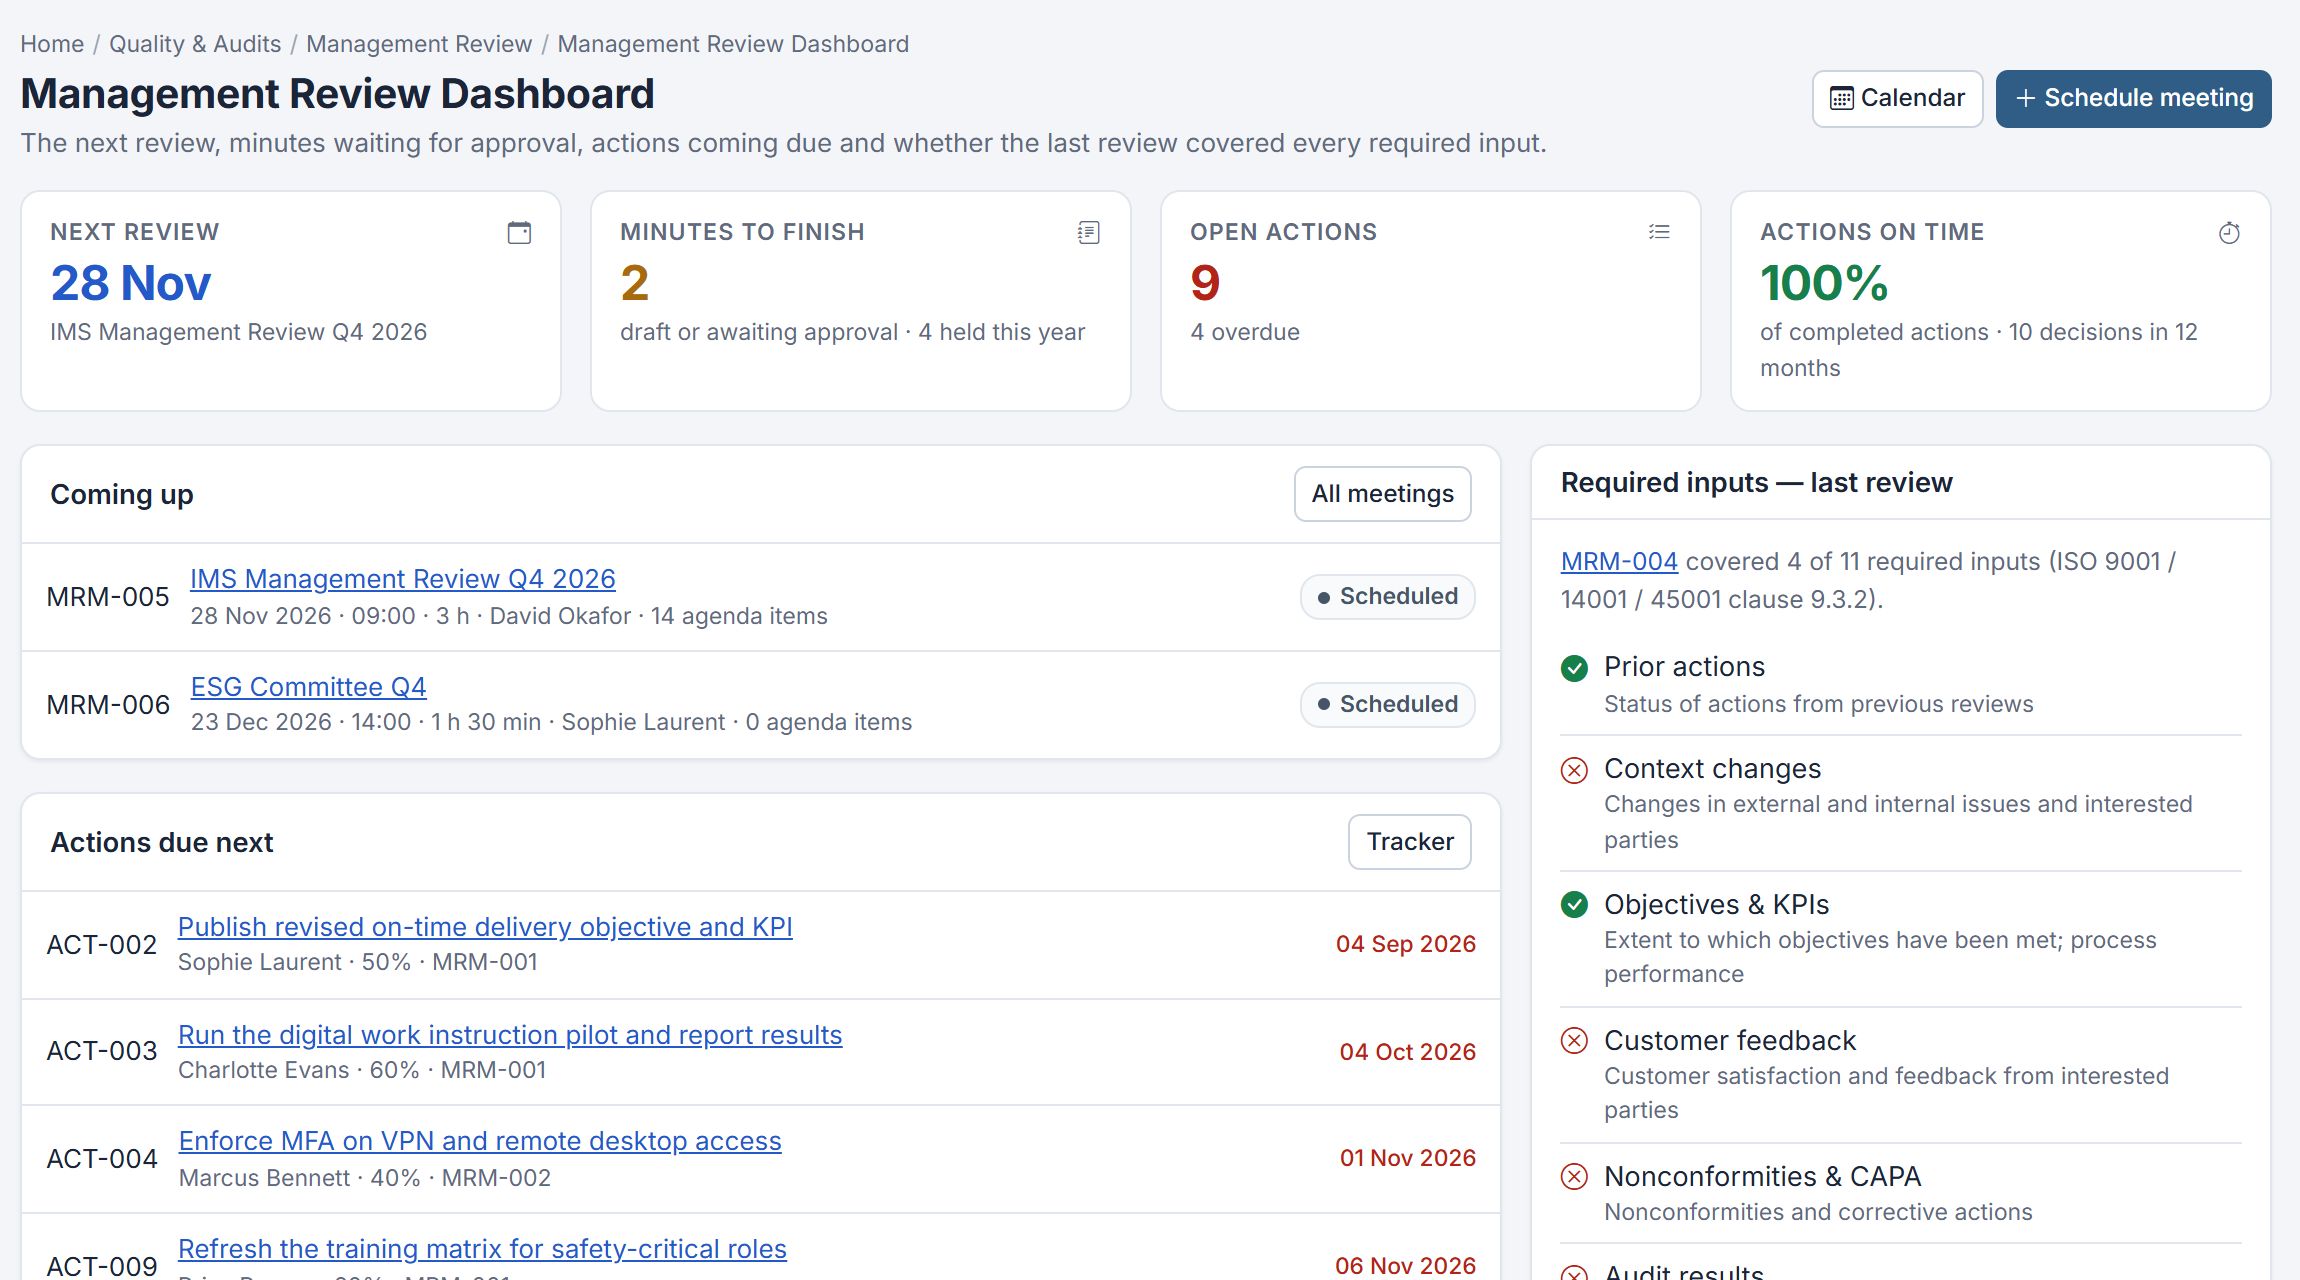
The inputs ISO 9001 clause 9.3.2 requires for management review, and how to build the agenda from live data on audits, actions, objectives and risks.
Management Review
What ISO 9001 clause 9.3.3 expects as management review outputs, how to record decisions and actions, and how to approve minutes auditors trust.
Cybersecurity
How to organise cybersecurity controls by the six NIST CSF 2.0 functions, Govern, Identify, Protect, Detect, Respond and Recover, alongside ISO 27001.
Project Management
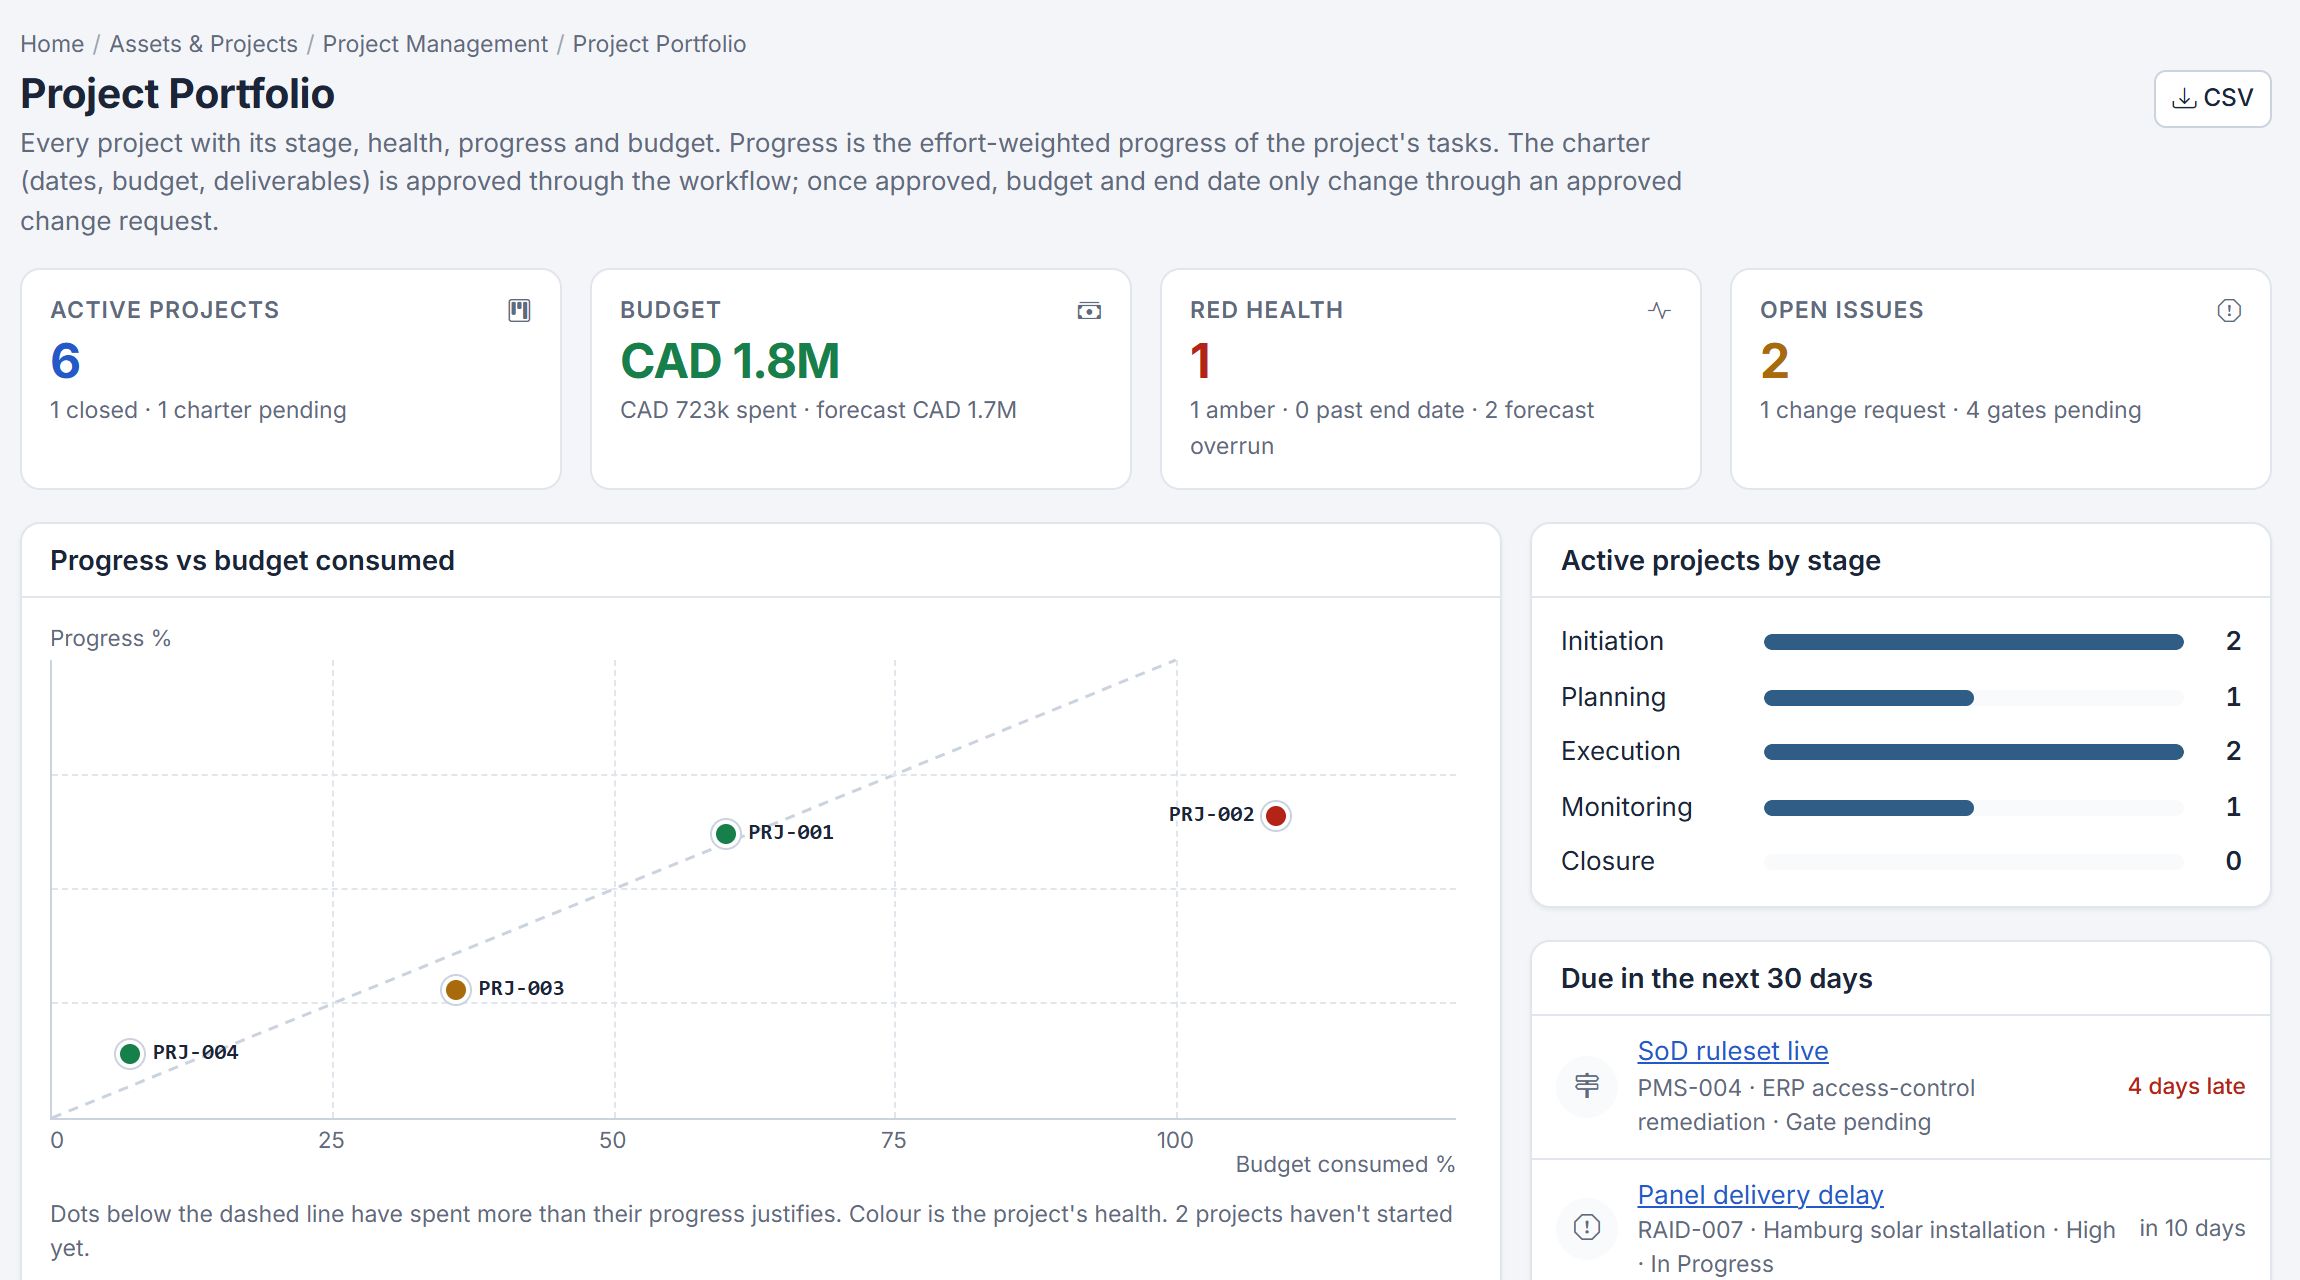
How to govern projects with an approved charter, a work breakdown, stage-gate approvals and resource balancing, in line with ISO 21502 guidance.
Business Continuity
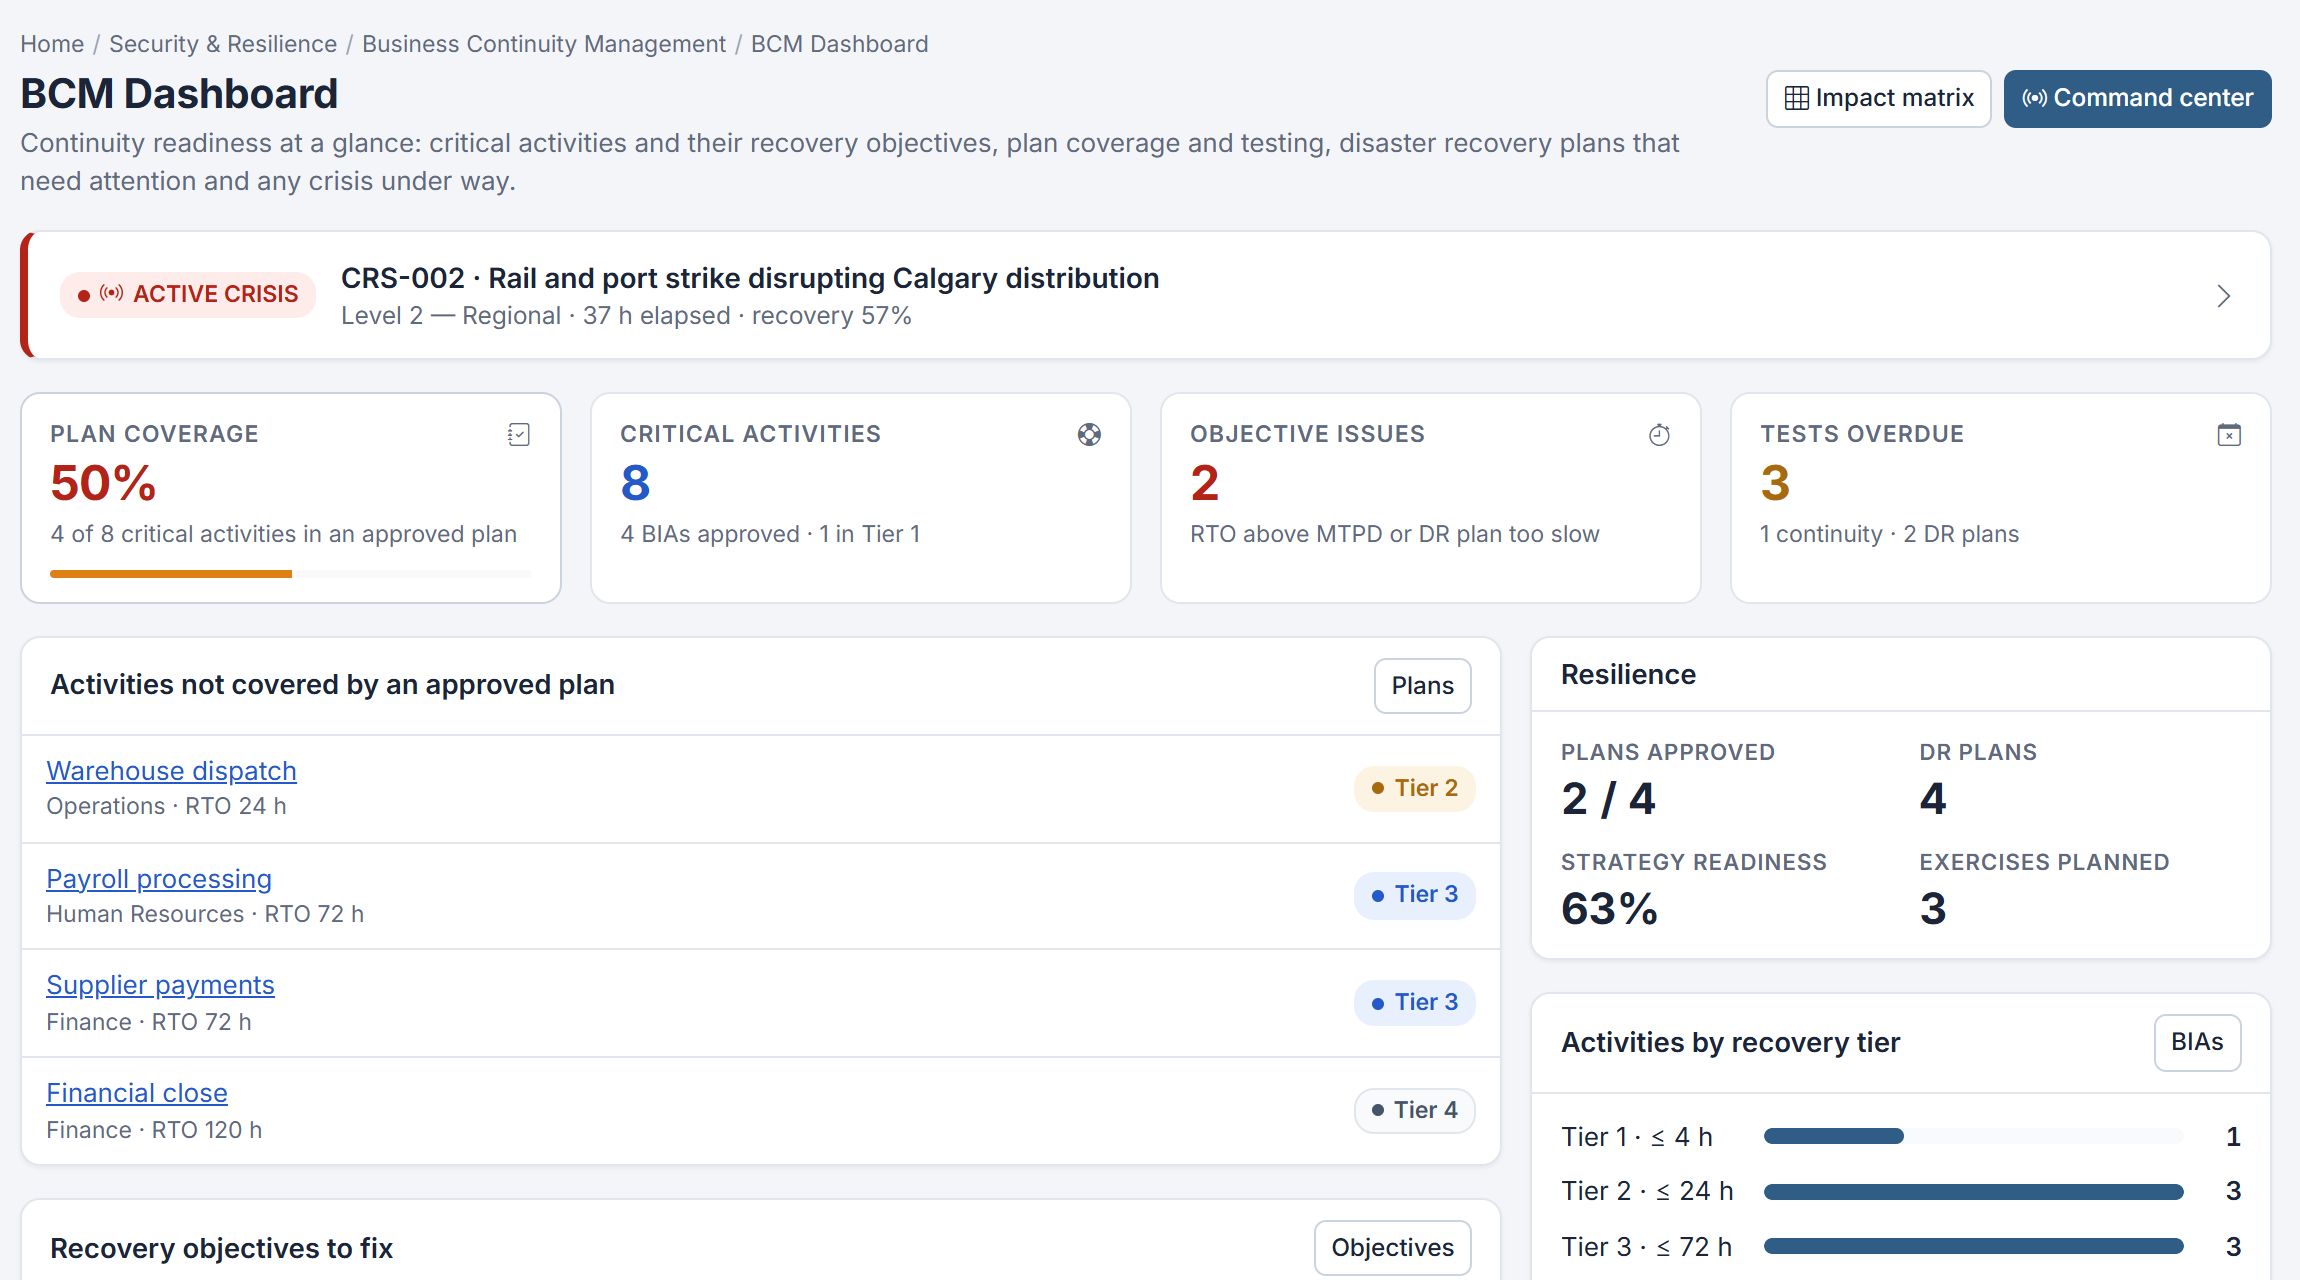
How to exercise continuity and disaster recovery plans under ISO 22301, from tabletop to live recovery, and run a real crisis with situation reports.
Human Capital
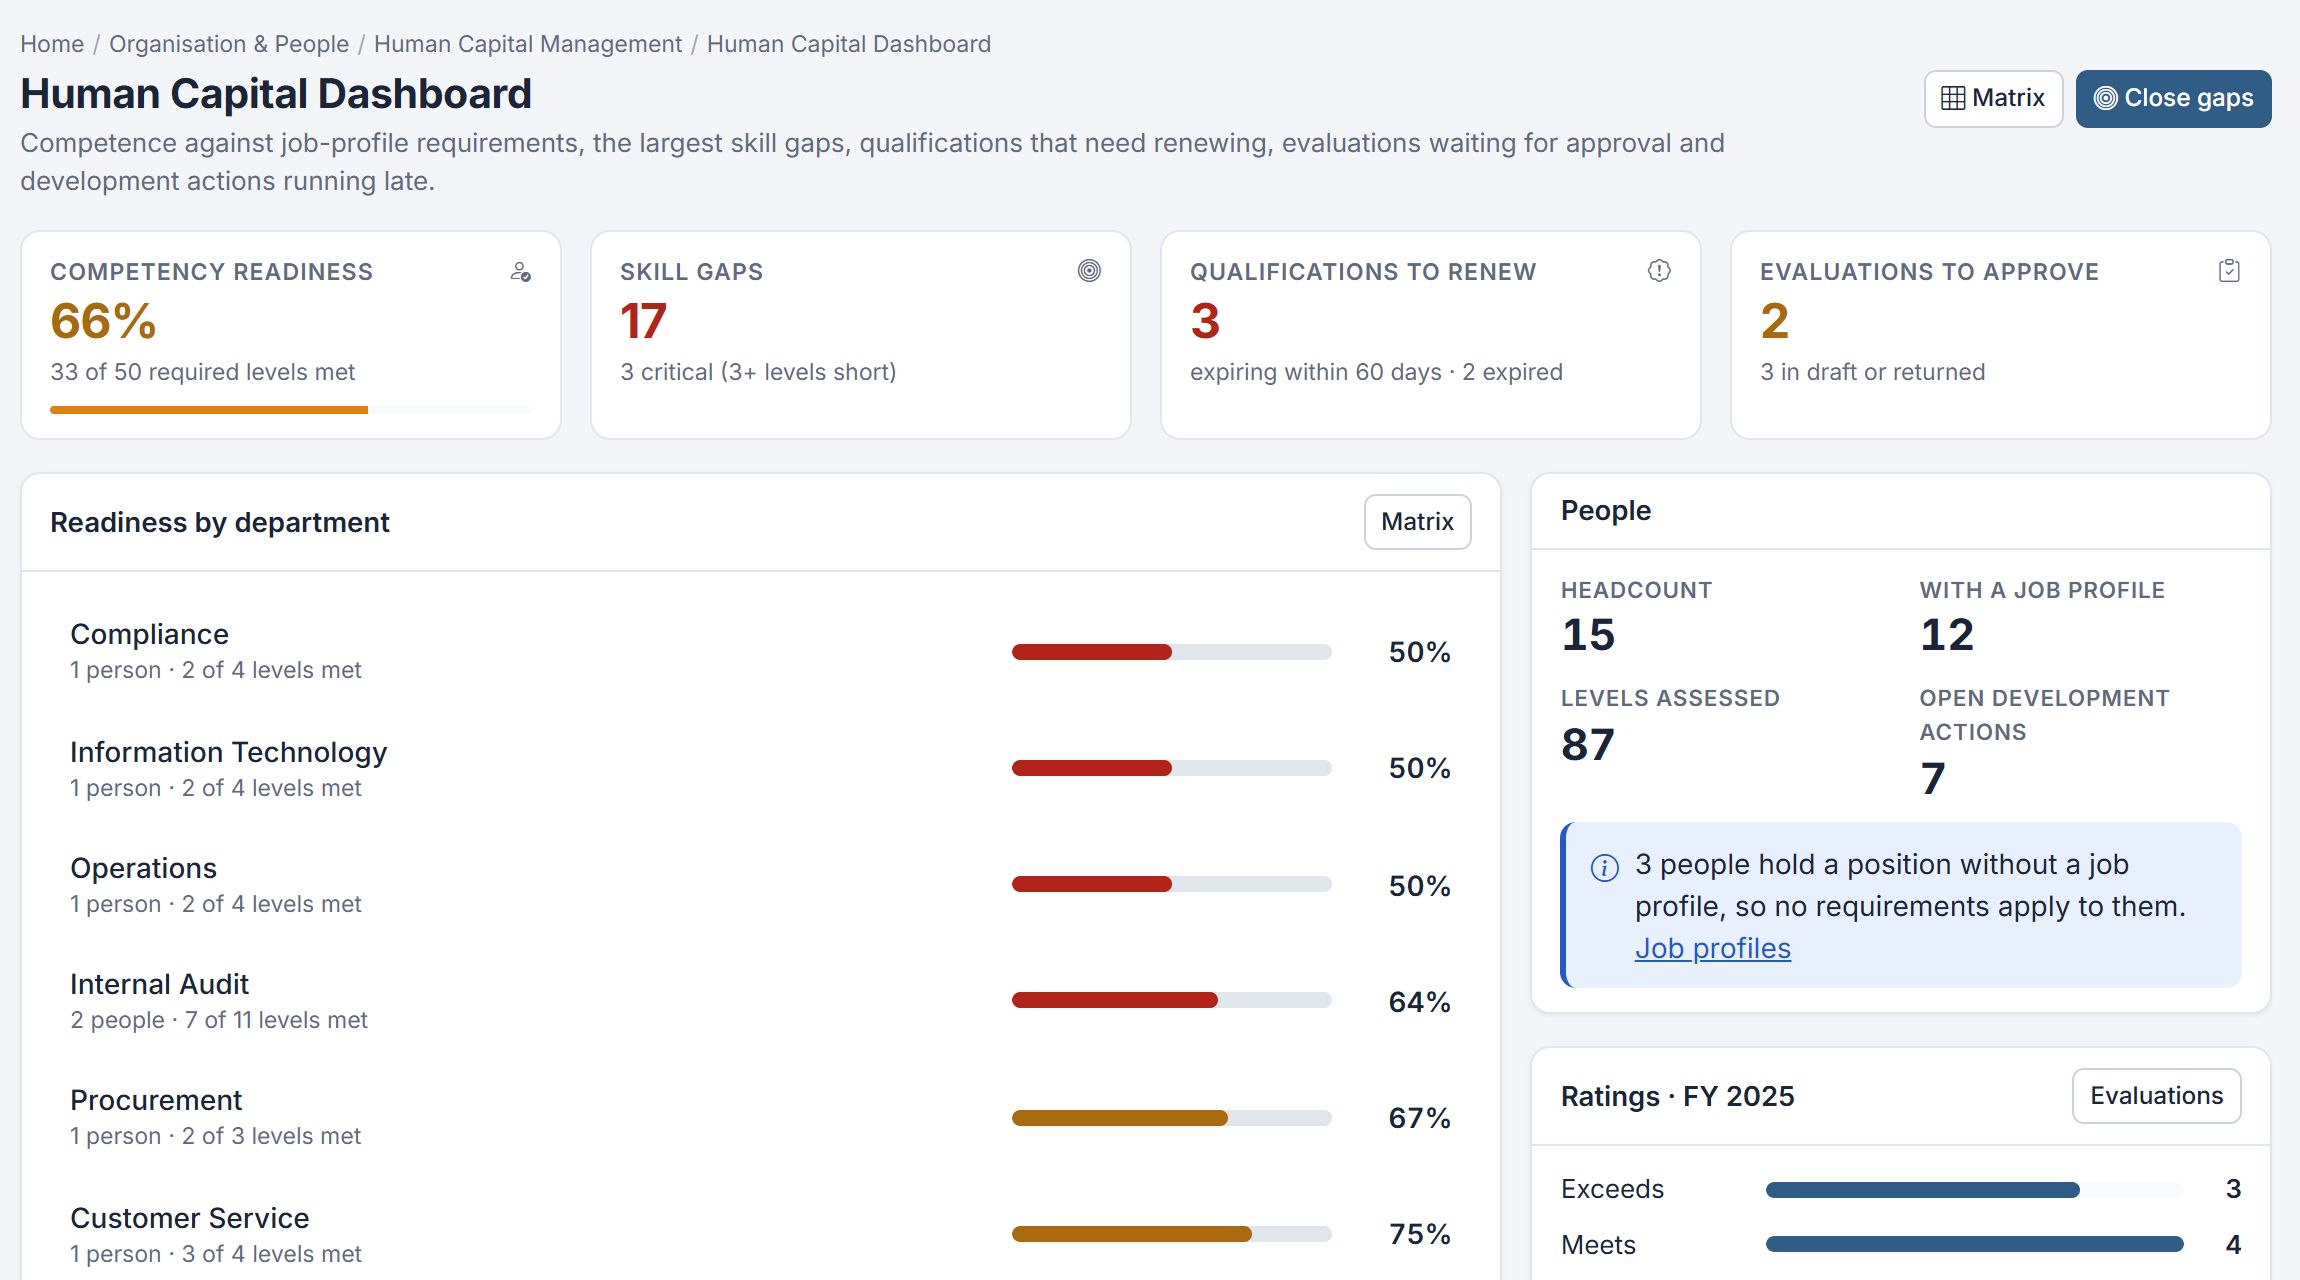
How to define competence requirements by role, assess people against them and keep the evidence ISO 9001 clause 7.2 asks for, beyond training certificates.
Reporting
Why traceability between audits, nonconformities, risks, documents and training matters for ISO audits, and how a relationship explorer shows the whole chain.
Incident Management
How to capture incident lessons learned, share them across sites and teams, and turn them into changes that prevent similar incidents elsewhere.
Reporting
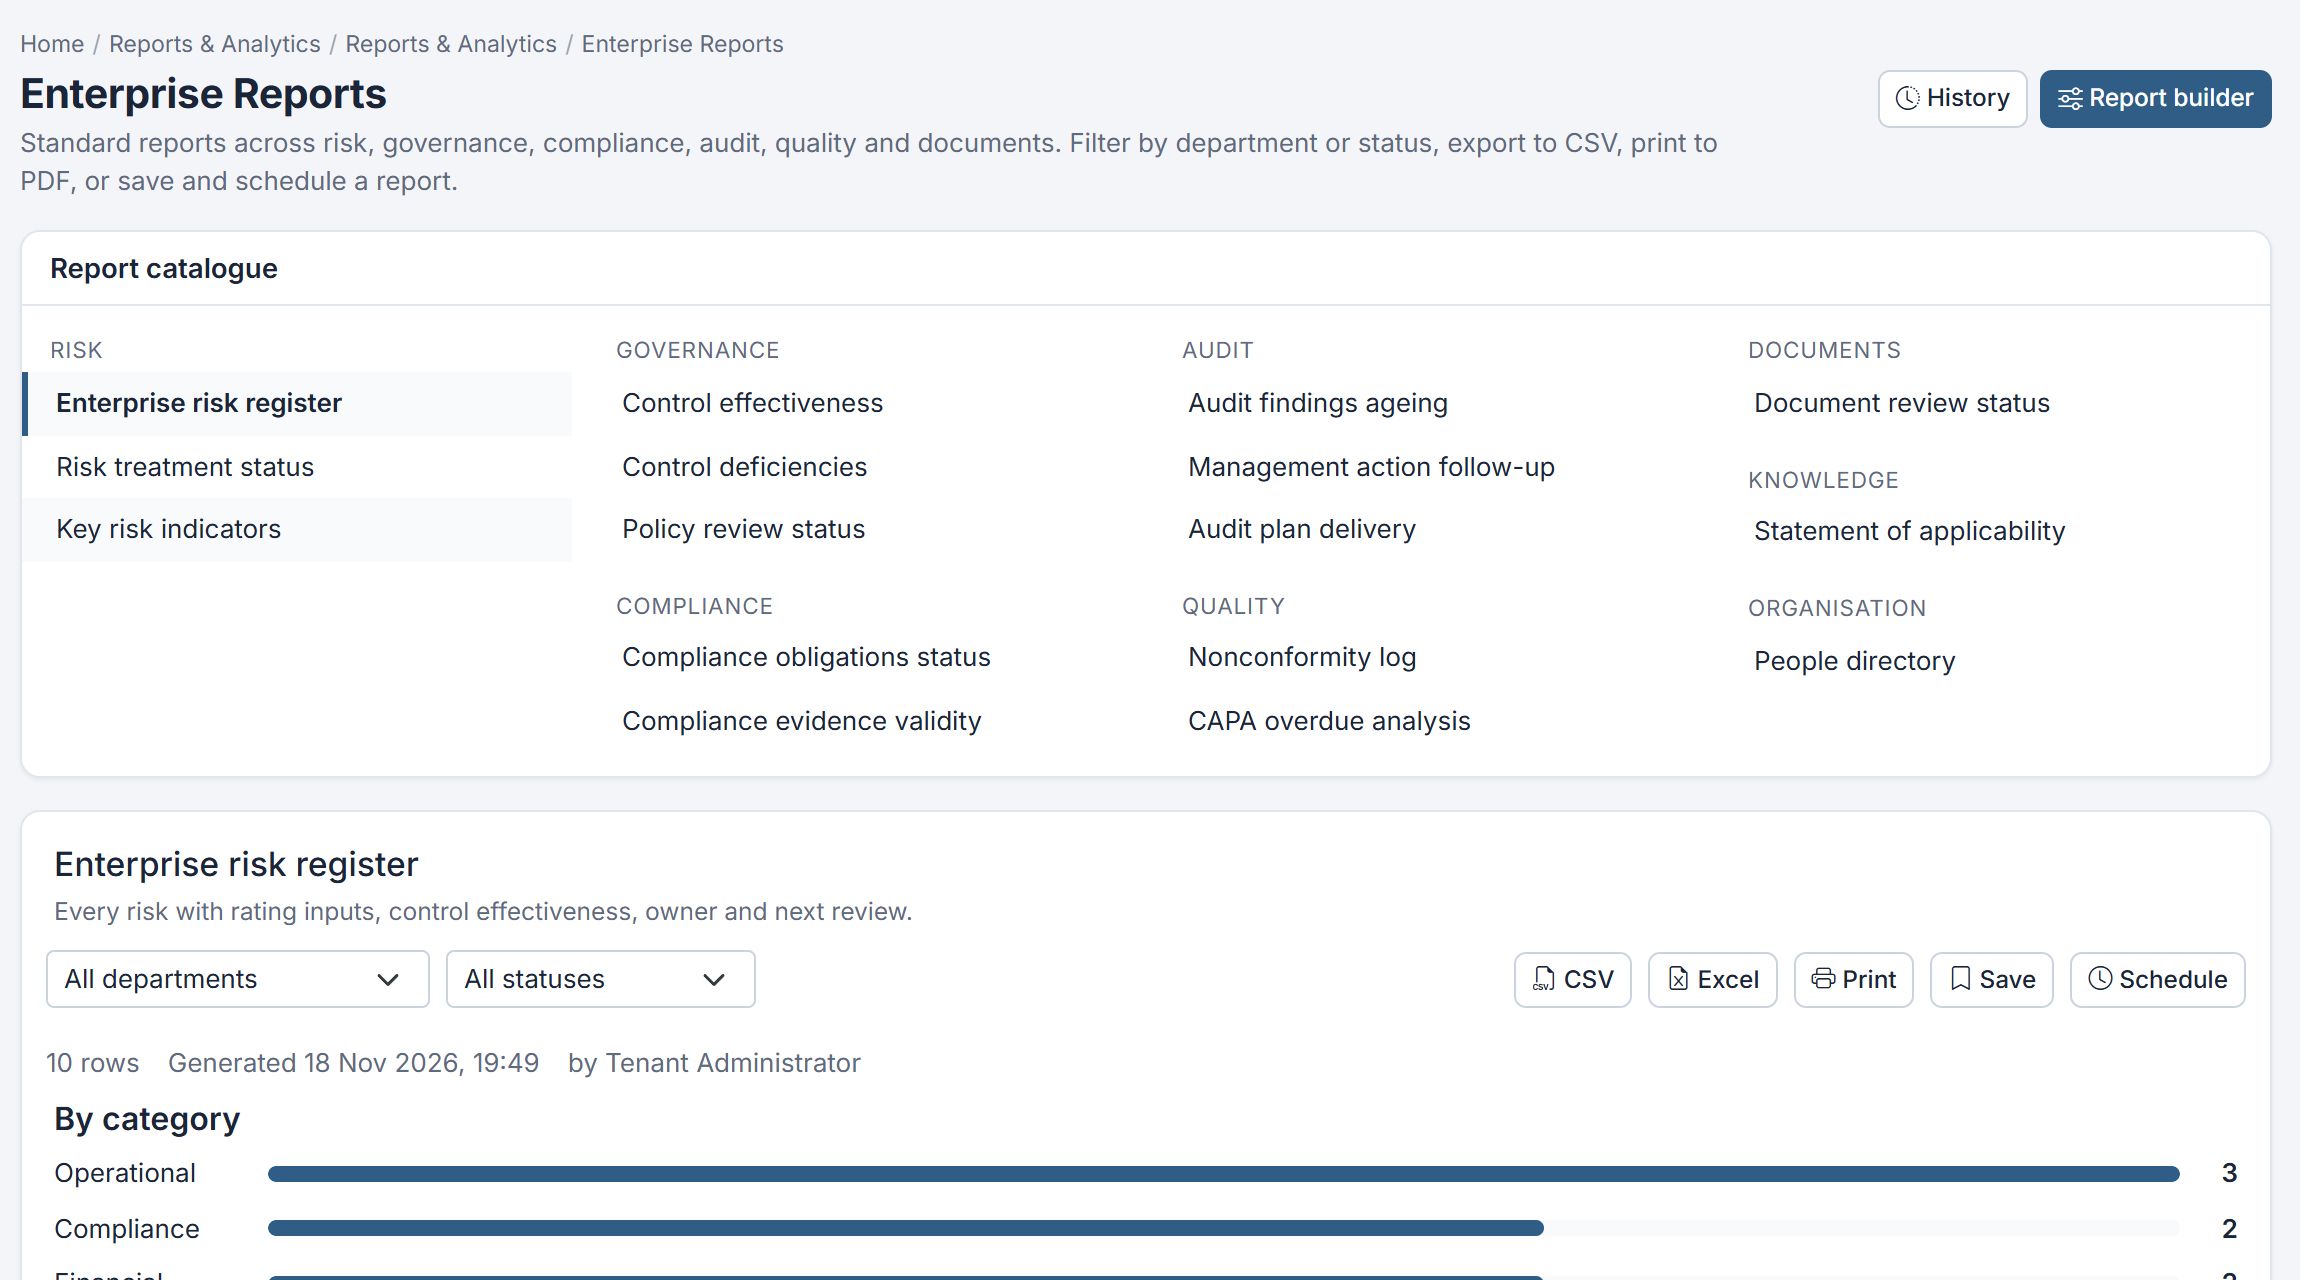
How to run quality management reporting with standard reports, a report builder, scheduled delivery and executive packs that support ISO 9001 clause 9.1.3.
Information Security
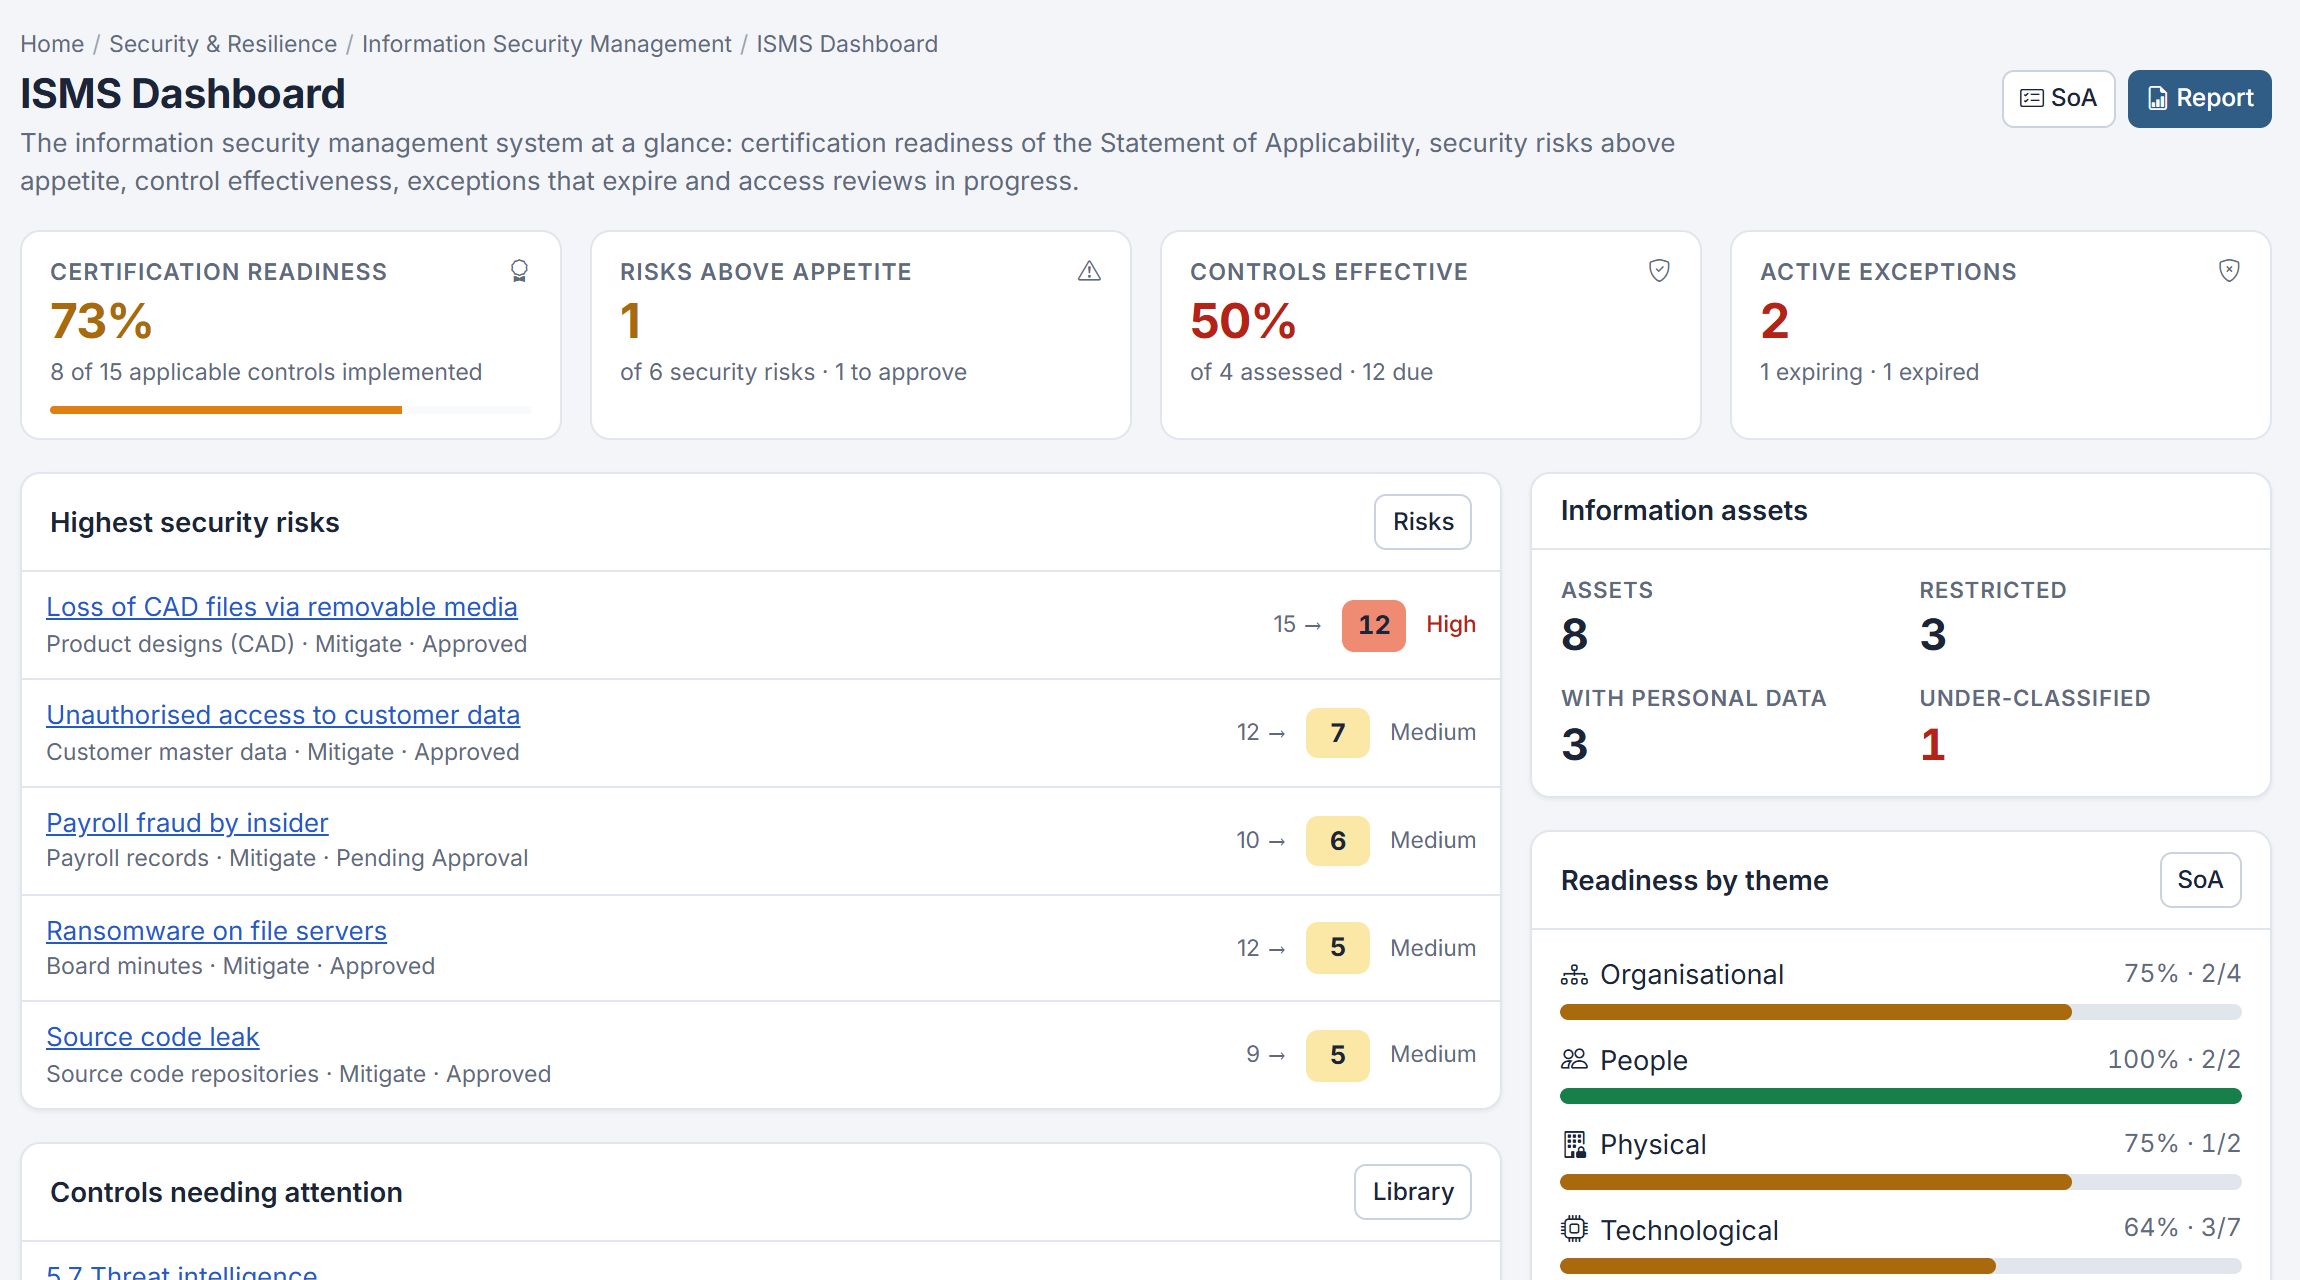
How to build and maintain an ISO/IEC 27001 Statement of Applicability: Annex A controls, justifications, implementation status and links to risk treatment.
Business Continuity
How to run a business impact analysis under ISO 22301: prioritised activities, impact over time, MTPD, RTO and RPO set consistently, and continuity strategies.
ESG & Sustainability
A practical approach to double materiality assessment: impact and financial materiality, stakeholder input, scoring, thresholds and links to ESG objectives.
Internal Audit
How to plan an ISO 9001 clause 9.2 internal audit programme that is genuinely risk-based, using an audit universe, priorities and the guidance in ISO 19011.
Training Management
How to evaluate training effectiveness for ISO 9001 clause 7.2 using assessments, observed performance and follow-up, not just attendance sheets.
Asset Management
How to manage calibration for ISO 9001 clause 7.1.5: equipment identification, traceable intervals, status, and handling out-of-tolerance results.
Project Management
How to control project budget and scope change, manage risks and issues, and close projects with lessons learned that improve future delivery.
Process Management
How to apply the ISO 9001 process approach (clause 4.4): process architecture, swimlane maps, owners, controls, risks and performance measures.
Knowledge Hub
Why breaking ISO standards and regulations into clause-level requirements helps you map controls, plan audits and manage new editions with less rework.
Environment
How to identify environmental aspects and impacts for ISO 14001 clause 6.1.2, assess significance consistently, and link aspects to obligations and controls.
ESG & Sustainability
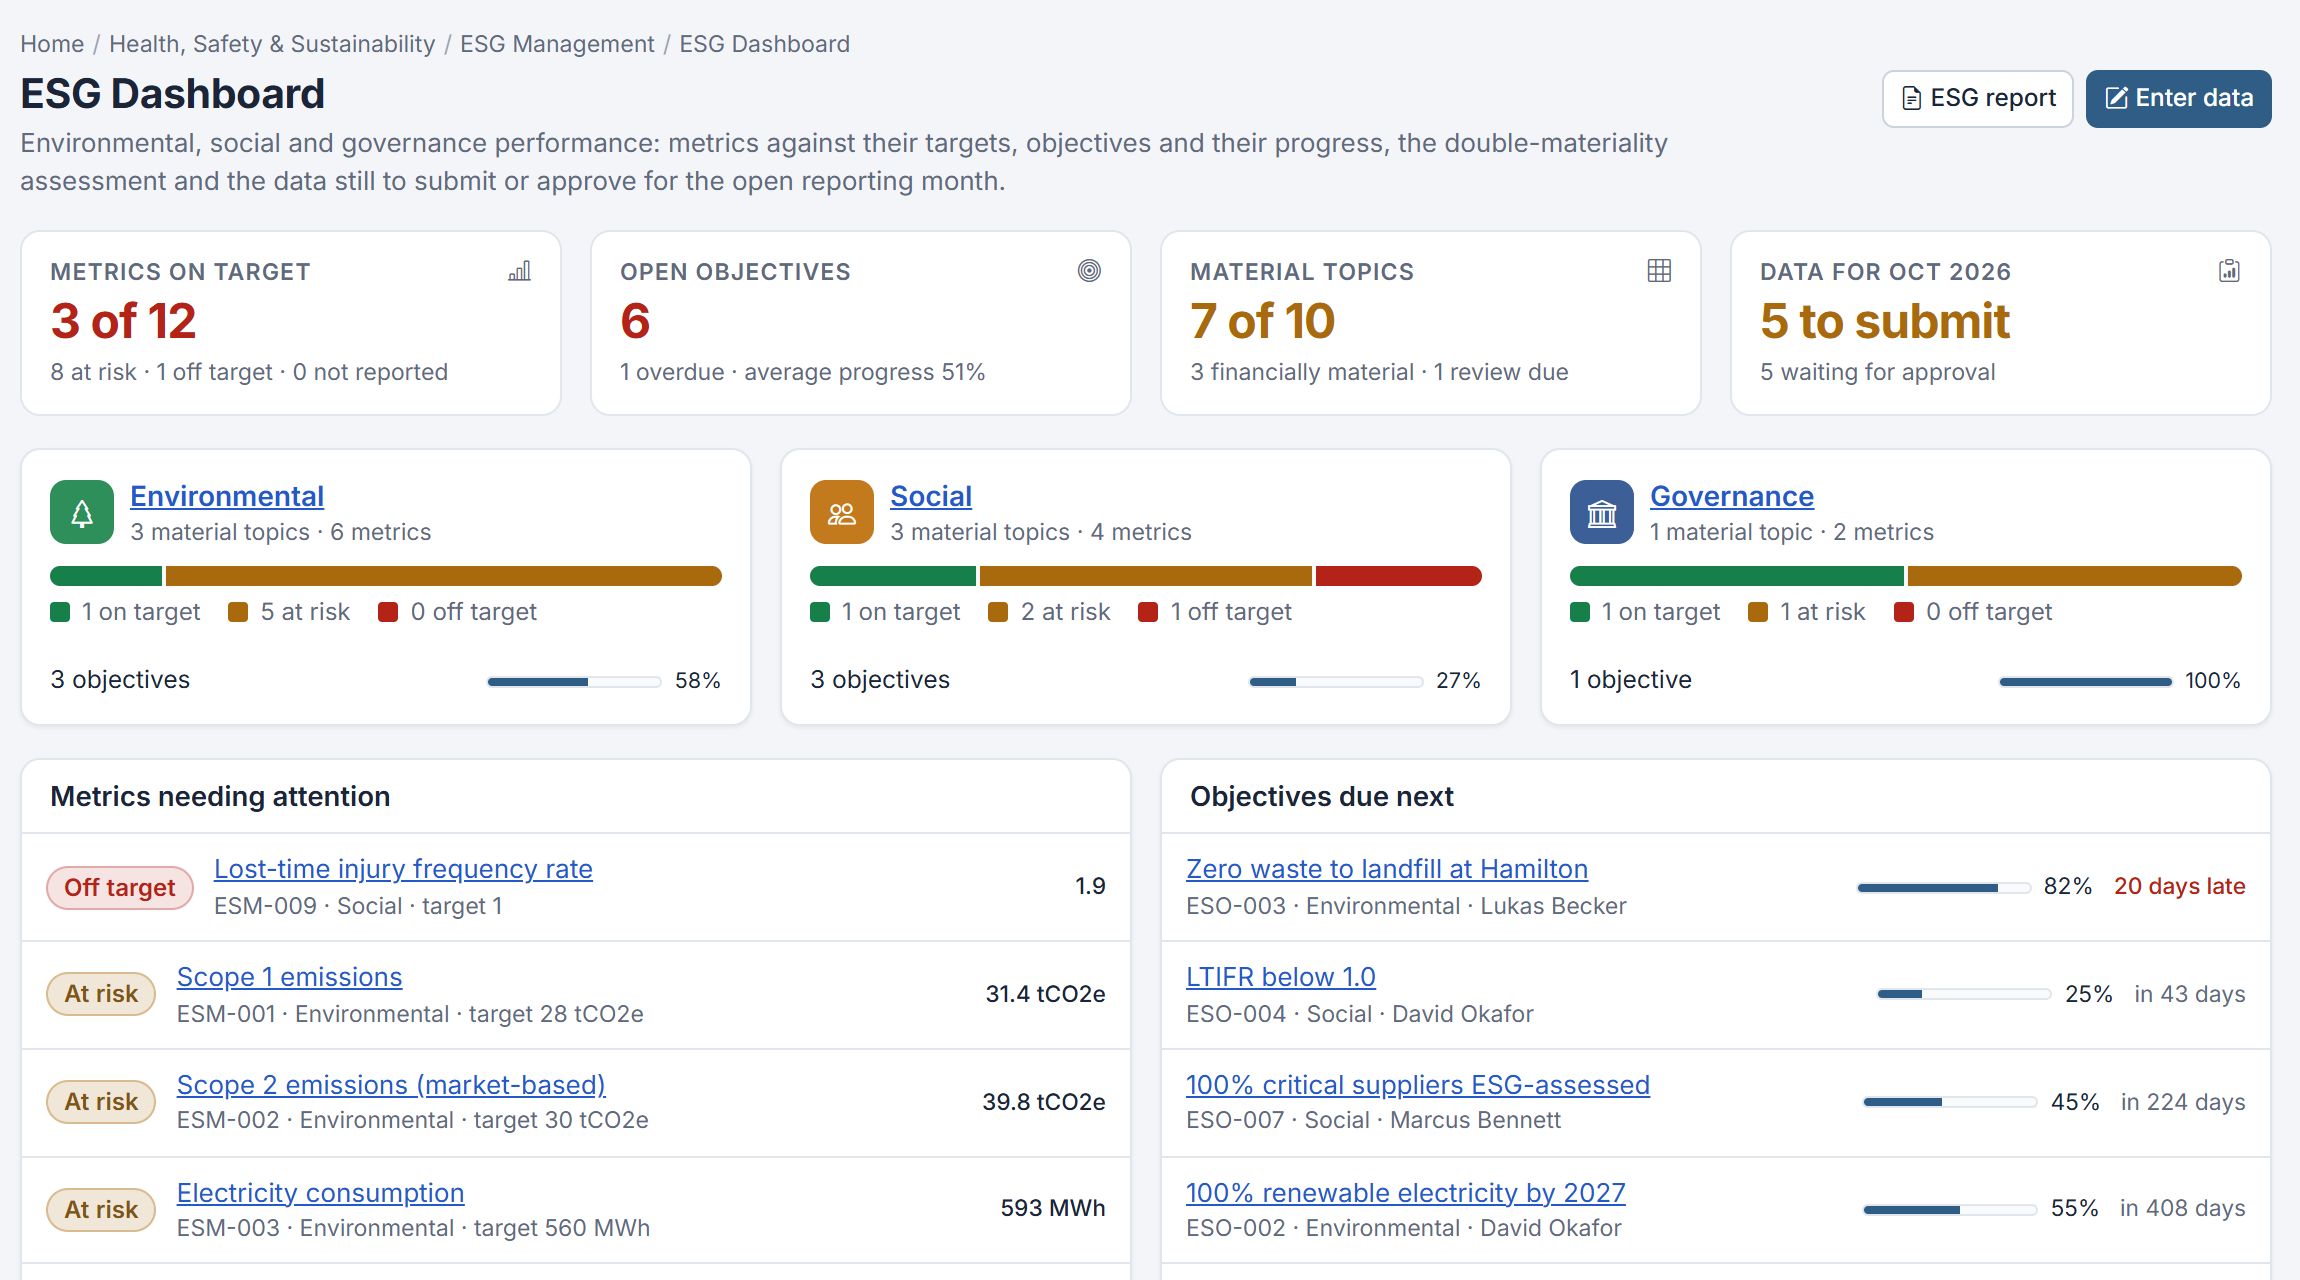
How to collect ESG metrics monthly with clear definitions, owners and independent approval, so sustainability data is reliable enough to publish and assure.
Compliance Management
A practical process for regulatory change management: monitoring sources, assessing impact, updating obligations and controls, and reporting to management.
Risk Management
What ISO 9001 clause 6.1 asks for on risks and opportunities, how to keep it proportionate, and how to connect risks to processes, actions and review.
Governance & Controls
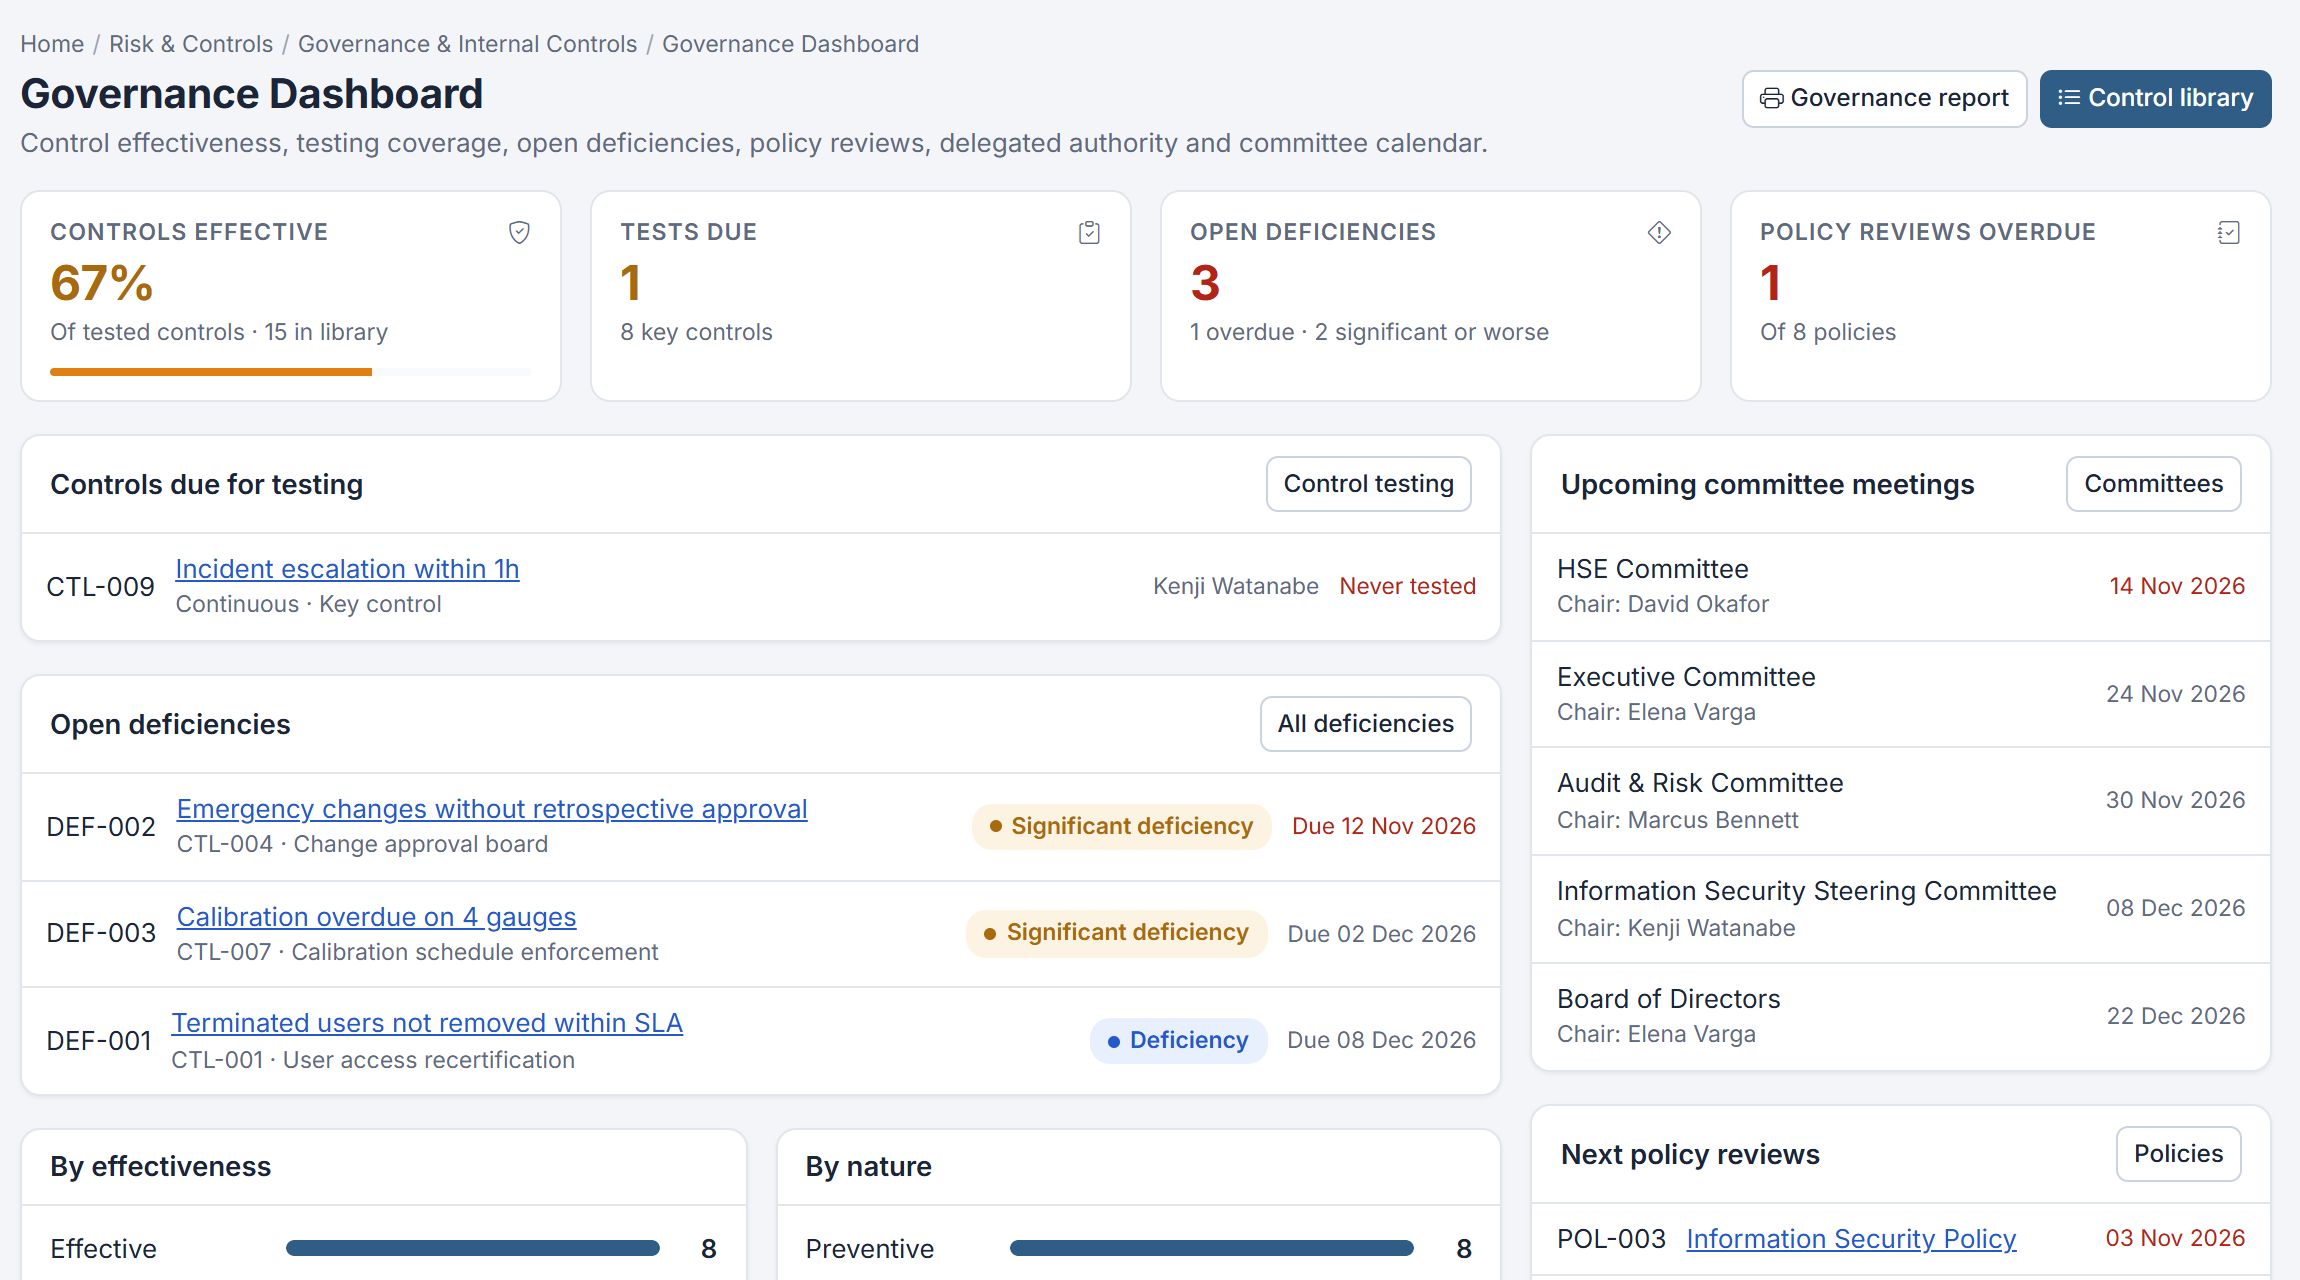
How to test internal controls for design and operating effectiveness, record deficiencies and verify remediation, using a control library aligned with COSO.
Supplier Management
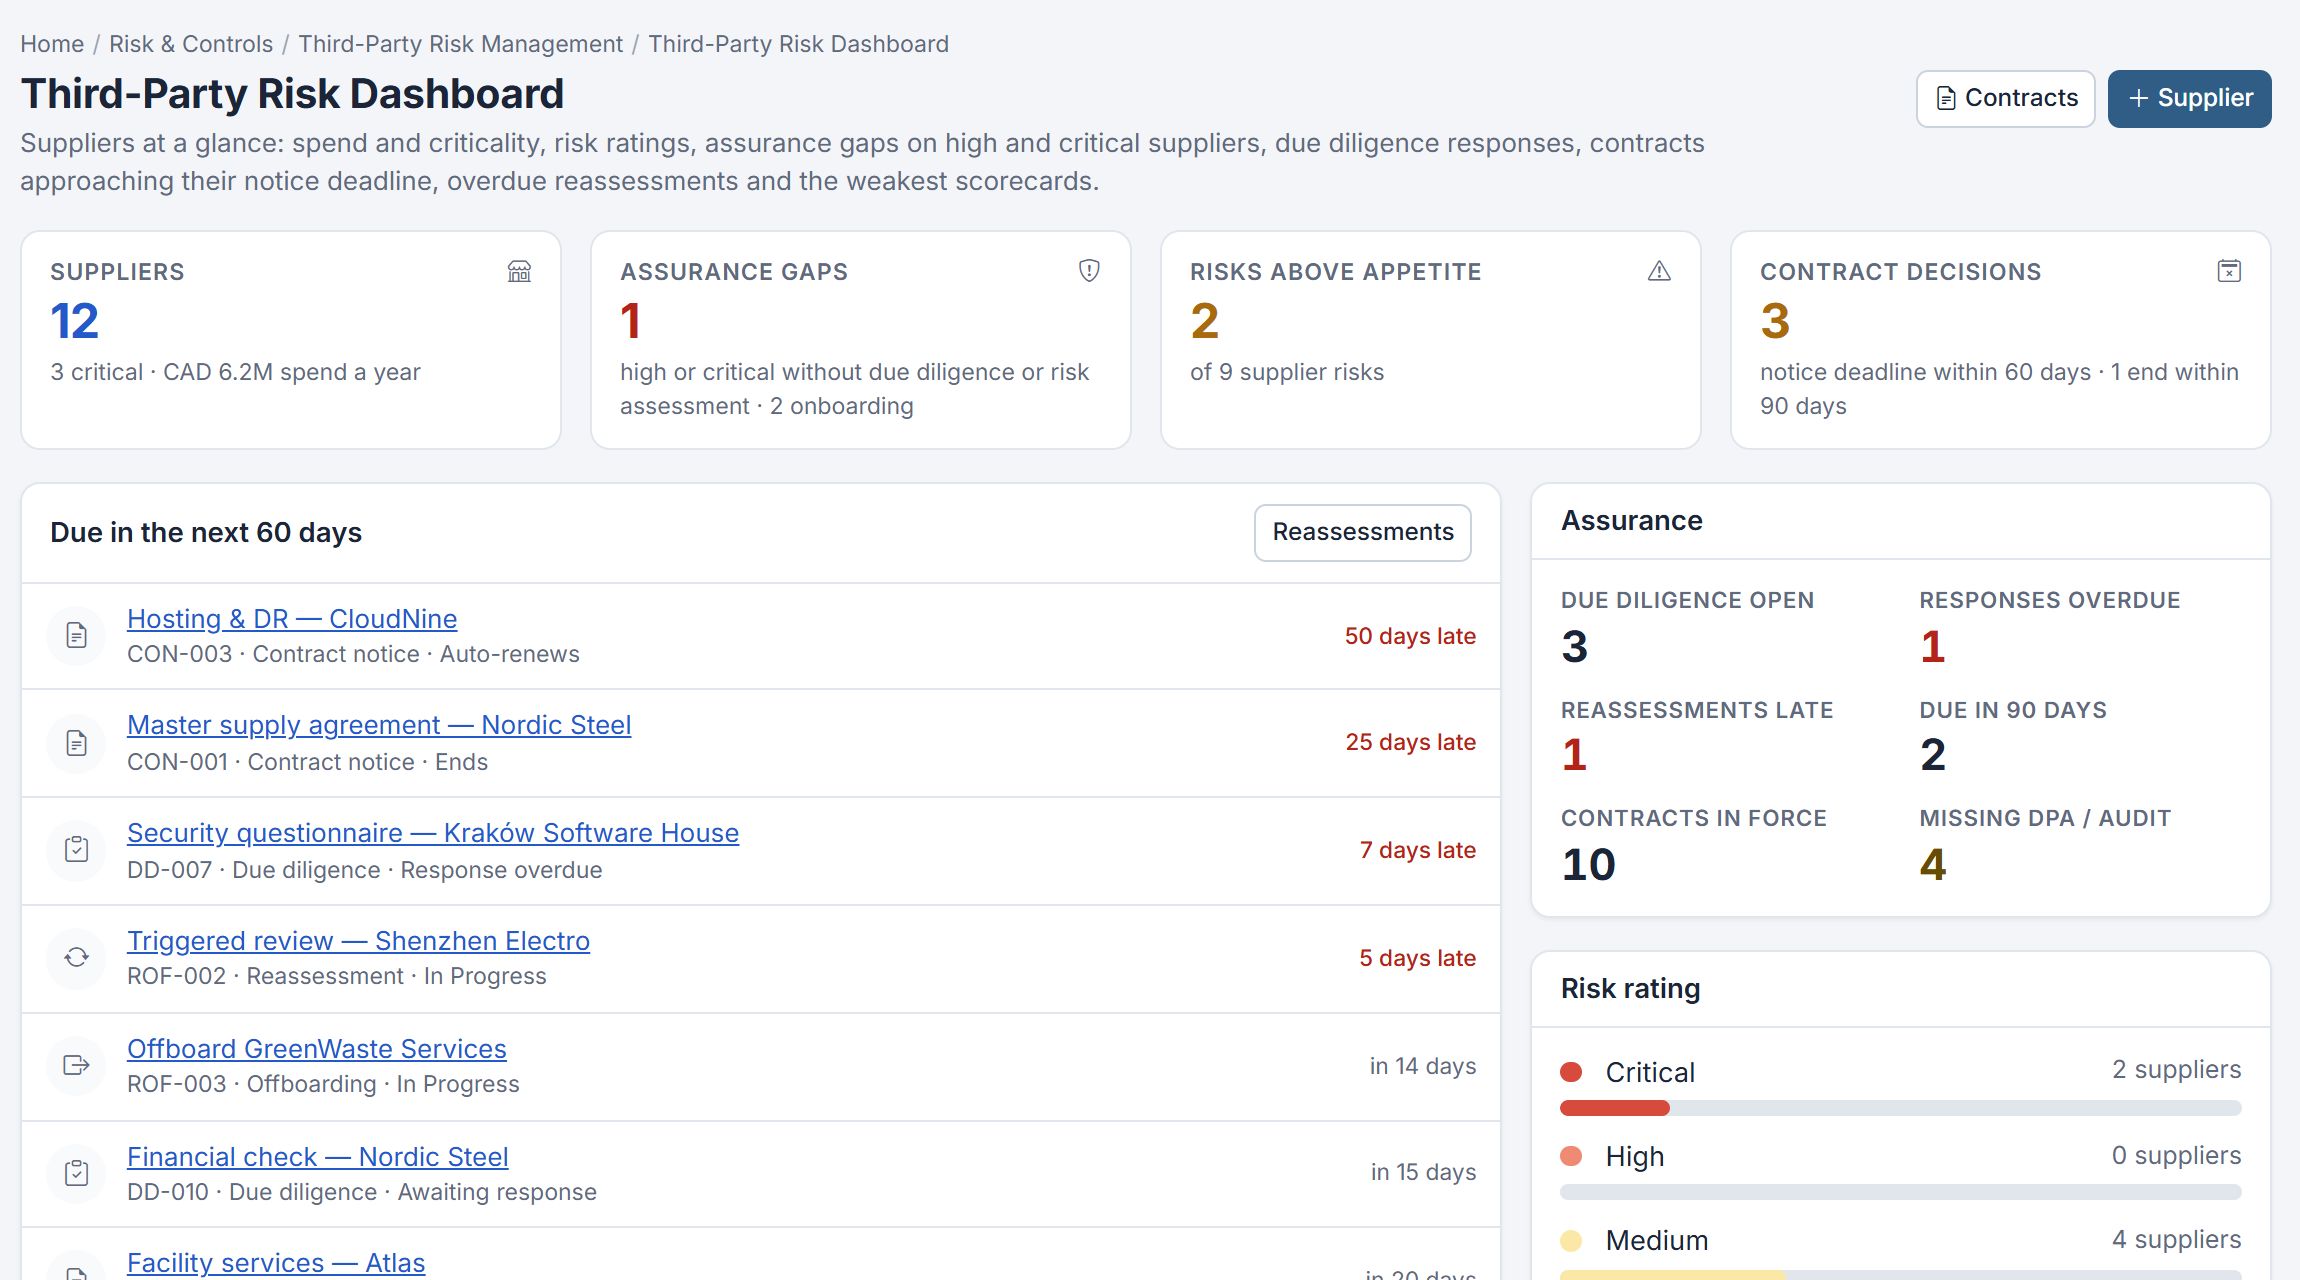
How to manage third-party risk across the supplier lifecycle: onboarding, contracts and SLAs, performance, reassessment and safe offboarding with data returned.
Human Capital
How to run a skills gap analysis that leads to action: role requirements, assessments, prioritised development plans and follow-up that closes the gaps.
AI Governance
Start AI governance with an AI system inventory: EU AI Act classification, ownership, controls mapped across ISO/IEC 42001 and NIST AI RMF, and clearance.
Customer Engagement
A practical complaint handling process aligned with ISO 10002: capturing feedback, response and resolution SLAs, root cause, corrective action and escalation.
Nonconformity & CAPA
How CAPA software supports ISO 9001 clause 10.2 with containment, 5 Whys and fishbone root cause analysis, and actions that remove the cause.
Health & Safety
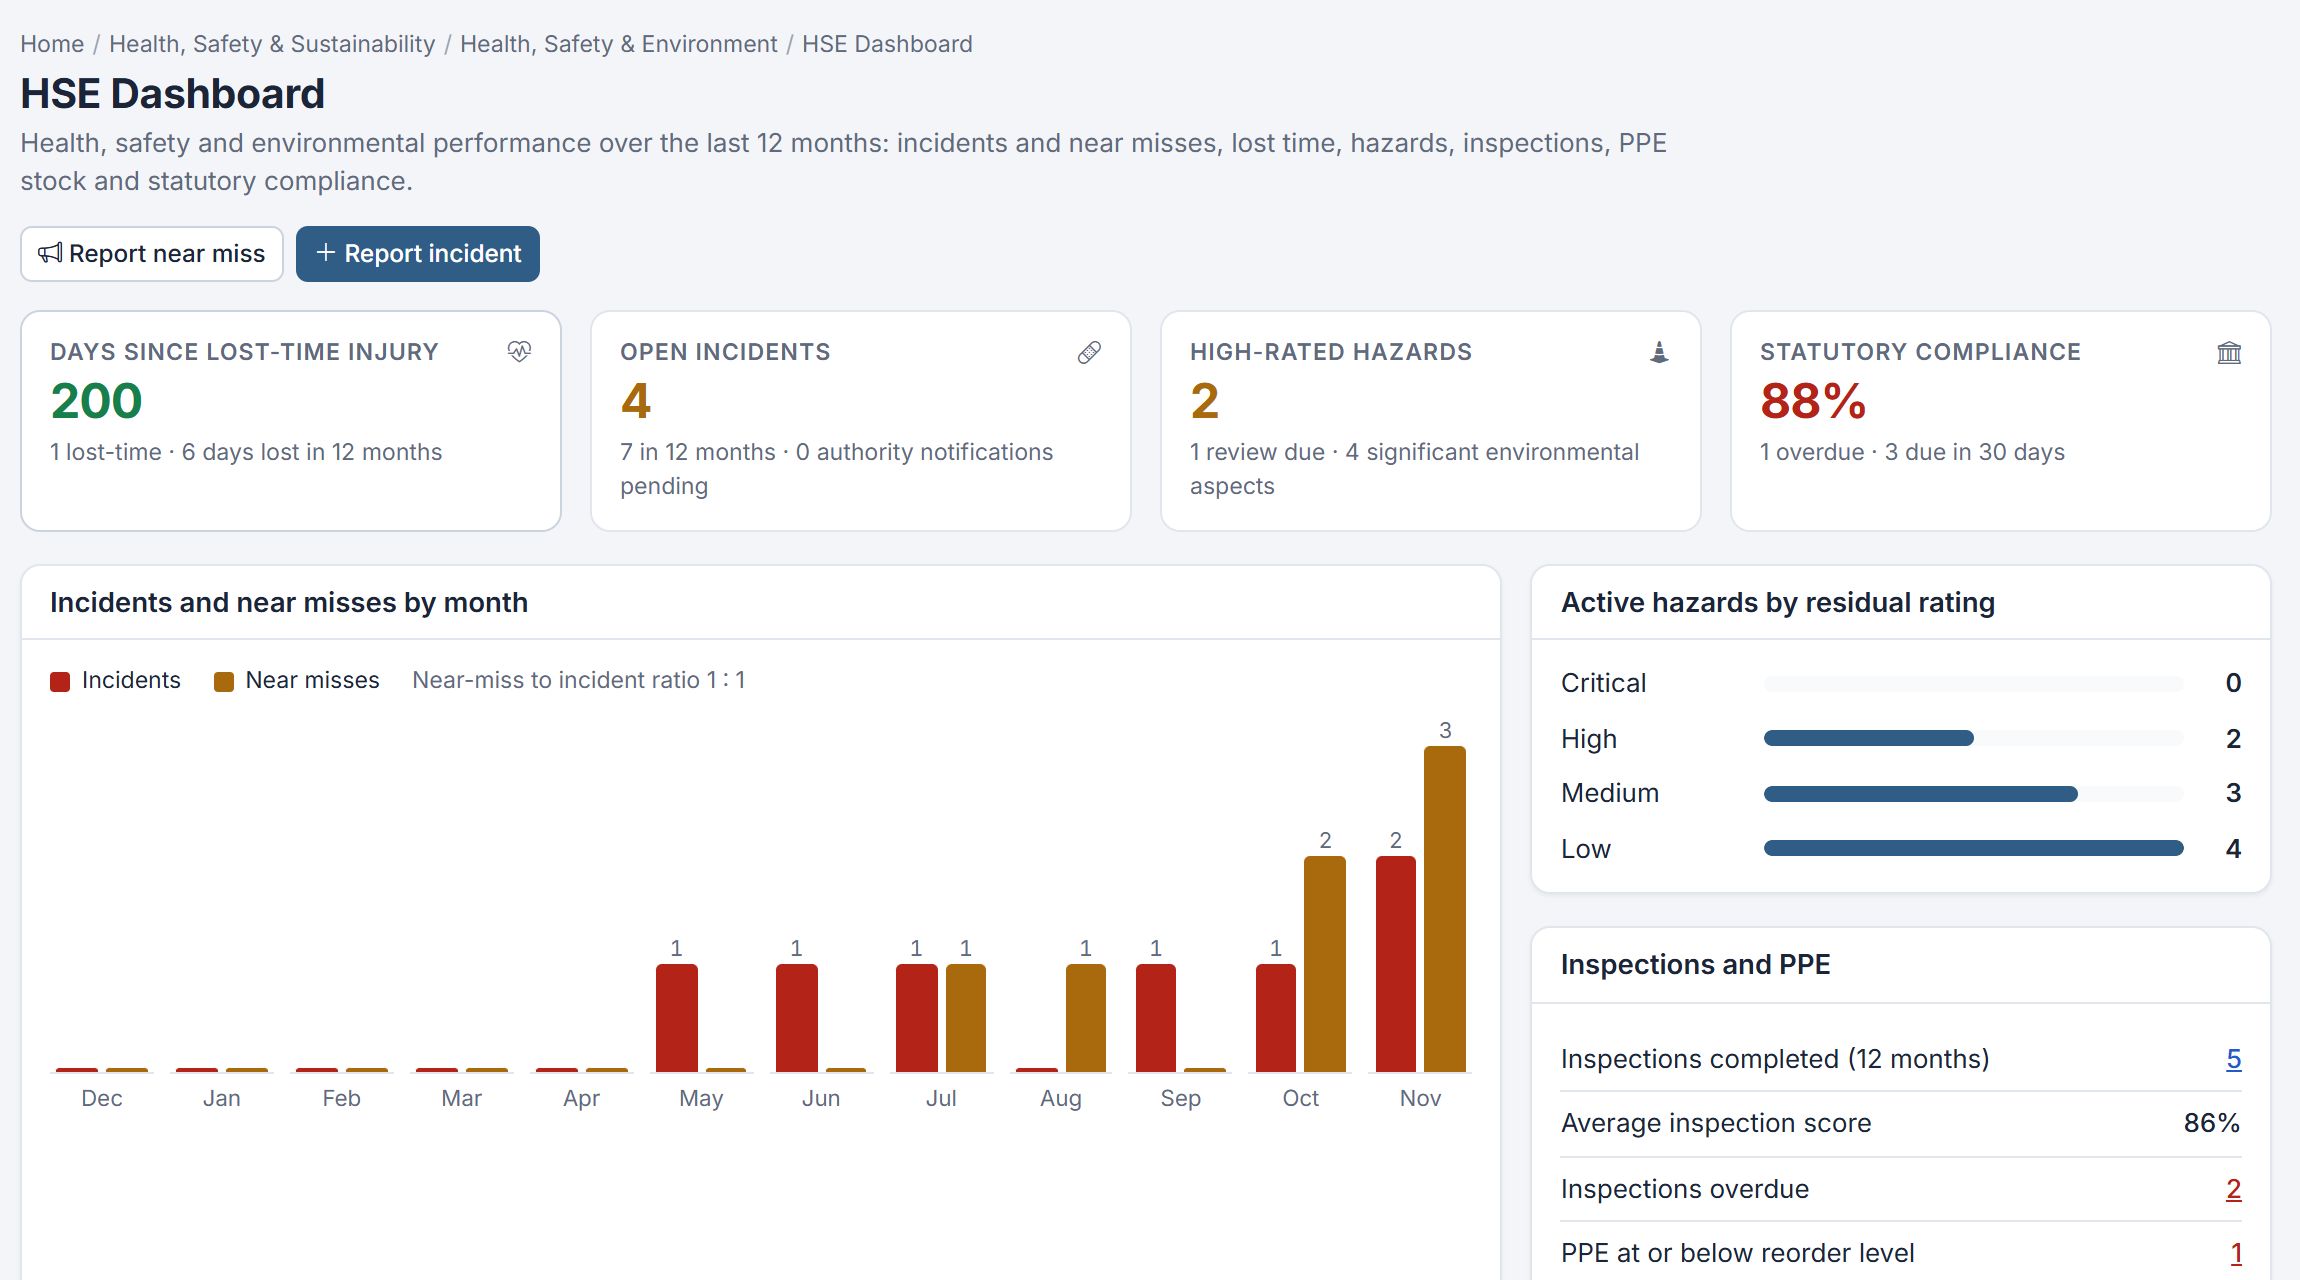
How to meet ISO 45001 clause 6.1.2: ongoing hazard identification, risk assessment, the hierarchy of controls, residual ratings, inspections and near misses.
KPI Management
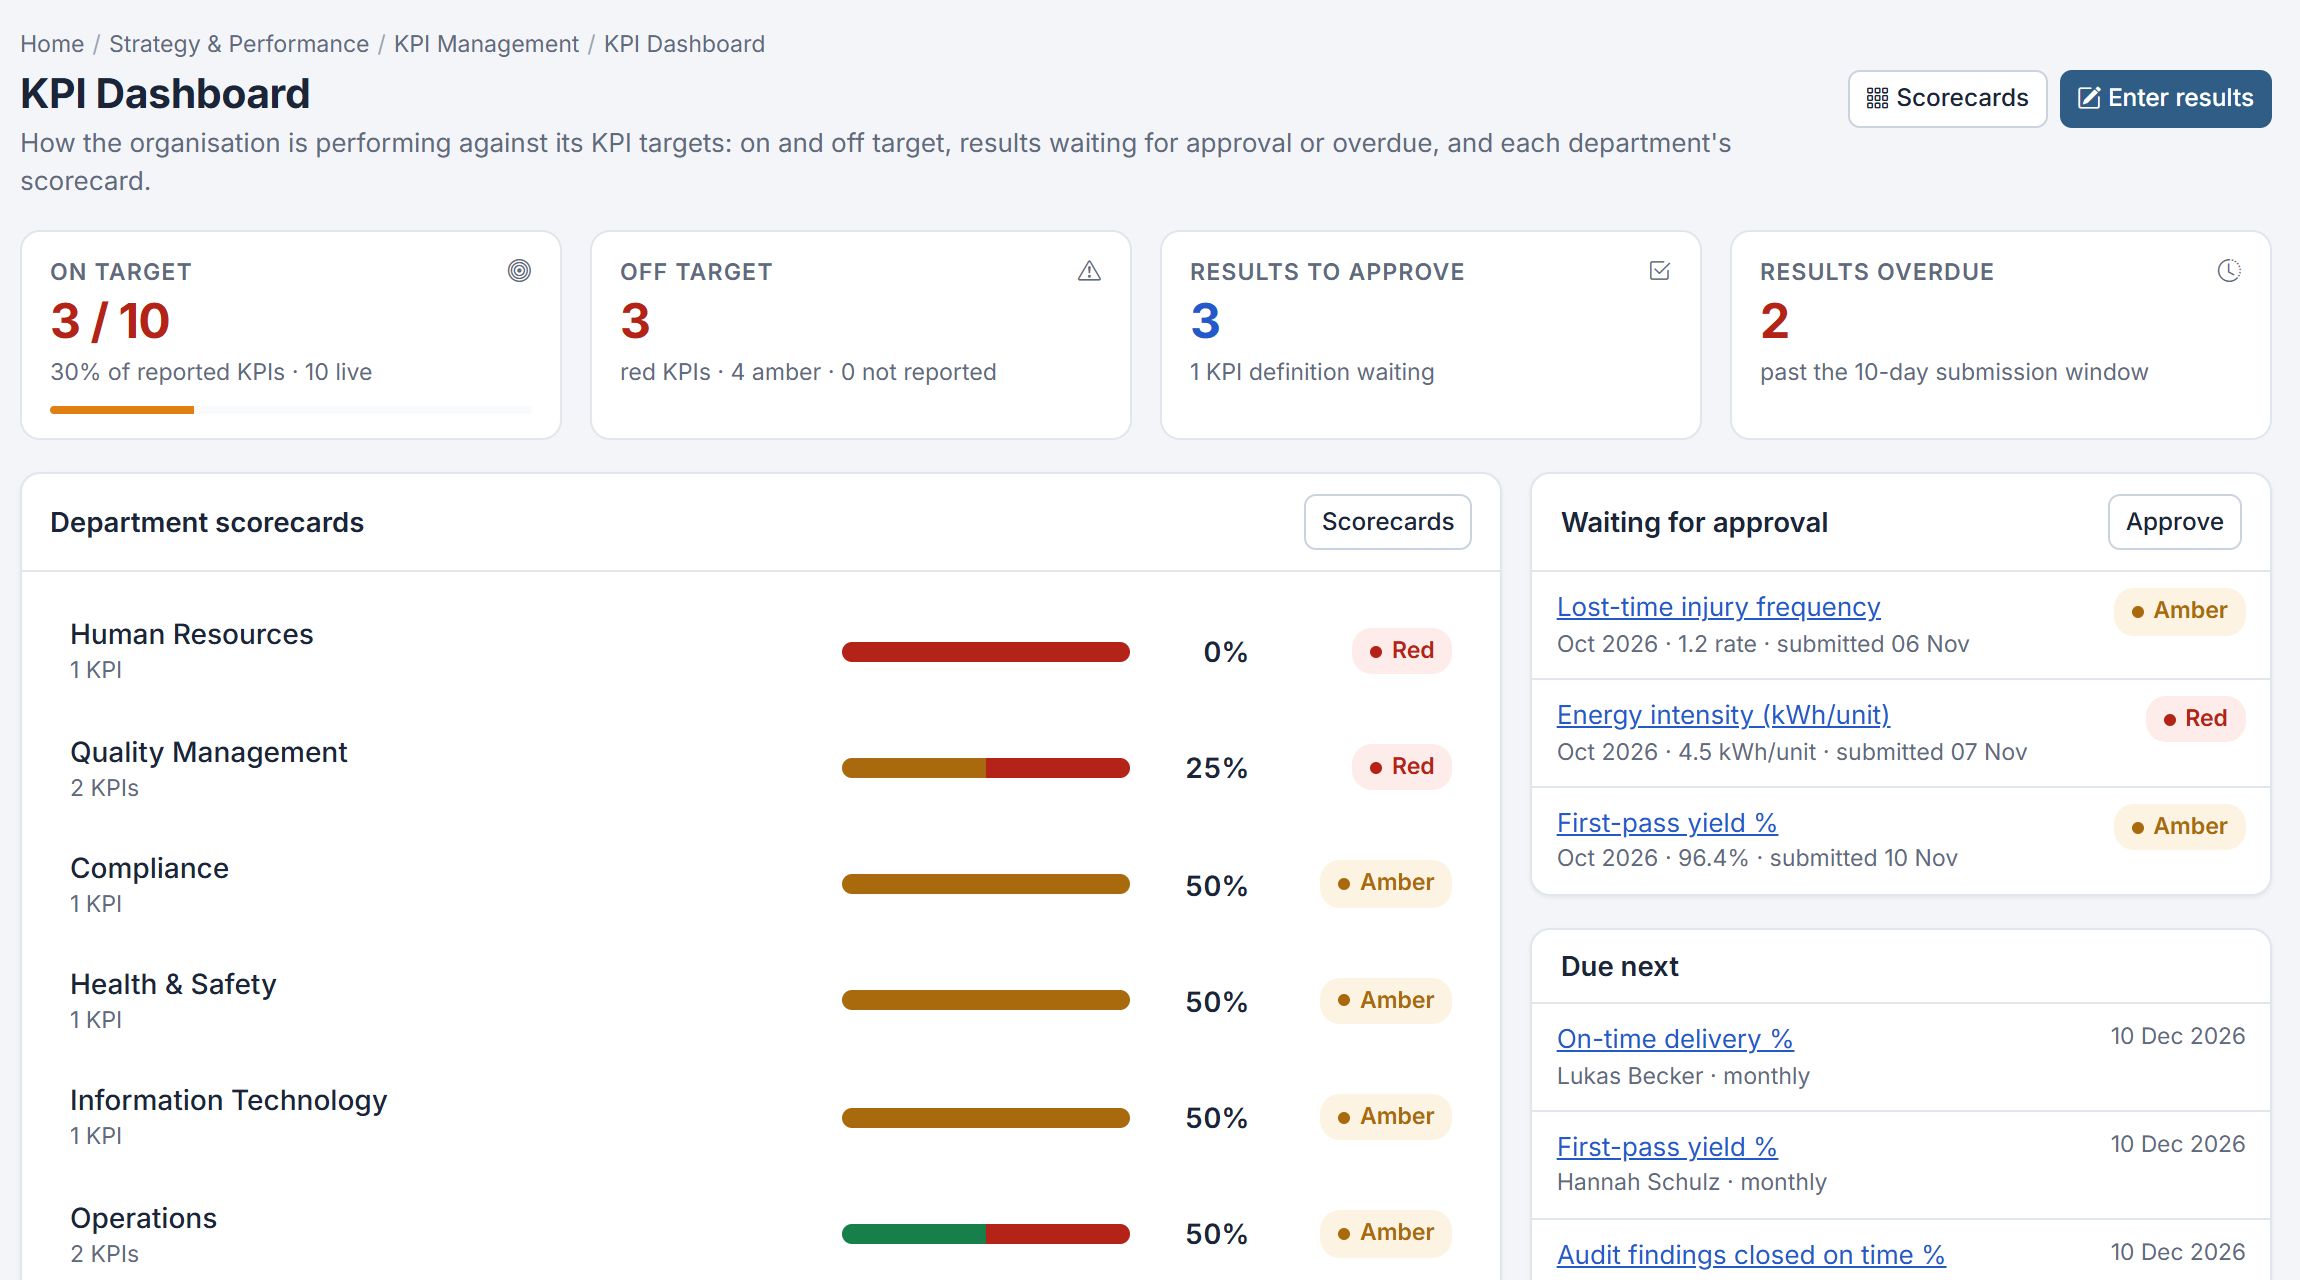
How to build red-amber-green KPI scorecards by department, review trends, and use frozen snapshots so performance reviews discuss the same numbers.
No articles in this area yet.
See it in context
We will walk through how your documents, audits, actions and risks would run in Certora, using the way your team works today.